

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.

Why Outside Feedback Makes Your Engineering Team Stronger
Casey Ellis delivered a talk at the 2017 Structure Security Conference addressing how external feedback strengthens engineering teams. He discussed methods for incorporating outside perspectives into development processes to improve security outcomes and team resilience.

SINET Thinks Forward: Human Versus Technology - What’s Next For Bug Bounty Programs
SINET61's SINET Thinks Forward conference in Sydney featured a stage discussion on the future of bug bounty programs. Casey Ellis spoke on the balance between human expertise and technological capabilities in security vulnerability discovery and management.
Security.txt Standard Proposed, Similar to Robots.txt
This BleepingComputer news article from September 2017 reports that web developer Ed Foudil submitted an IETF draft to standardize security.txt, a root-hosted file describing a site's security policies. In it, Casey Ellis advises Foudil to axe first and then sandpaper, refining his many ideas one by one into a well-thought-out draft.

What are the latest cutting edge technologies in cybersecurity and the greatest needs?
The 8th Annual Billington Cybersecurity Summit featured a panel discussion on cutting-edge cybersecurity technologies and critical industry needs. Casey Ellis participated in the conversation addressing emerging threats and technological solutions in the cybersecurity landscape.

Nine Ways Tech Companies Can Stay Ahead Of The Curve
This Forbes Technology Council article from September 12, 2017, presents nine ways technology companies can stay ahead of rapid change in the industry. Casey Ellis of Bugcrowd advises technology executives to ask dumb questions when needed, decide which advice to ignore or adopt, and get a coach who keeps them accountable.

Casey Ellis - 5,500 Hackers + Your Code
SOURCE Security Conference Boston 2014 featured a presentation by Casey Ellis on coordinating security research at scale. Ellis discussed methods for managing bug bounty programs with thousands of participating researchers and integrating their findings into development workflows.

Planning To Grow Your Tech Business Team? Here's What To Look For When Interviewing
This Forbes Technology Council article from September 2017, titled "Planning To Grow Your Tech Business Team? Here's What To Look For When Interviewing," offers hiring guidance for tech business leaders. Casey Ellis of Bugcrowd contributes a point on tenacity, calling it an ingrained trait that cannot be taught.
Exclusive: Top Hackers-for-Hire Startup Names New CEO | Fortune
This Fortune article from August 28, 2017 reports that Bugcrowd, a bug bounty startup, is naming a new chief executive. Casey Ellis, the company's founder and former CEO, told Fortune he is stepping aside to become chairman and chief technology officer so he can focus on the technical product.
Rapidly growing bug bounty company Bugcrowd names new CEO
This CyberScoop article from August 28, 2017, reports that California-based bug bounty platform Bugcrowd named a new chief executive, Ashish Gupta. Casey Ellis, who helped launch the company in 2012, stepped down as CEO to become chairman and chief technology officer, and he says he approached the board with the idea months earlier.

Bugcrowd Launches Bug Bounty Program for Wi-Fi Device Maker eero
Dark Reading reported on Bugcrowd's launch of a public bug bounty program for Wi-Fi device maker eero in August 2017. Casey Ellis, Bugcrowd's founder and CTO, discussed the program's role in improving security for connected home devices through crowdsourced vulnerability research.
Voice of Security Radio: Finding Flaws in the IoT
Dark Reading's Voice of Security Radio broadcast Finding Flaws in the IoT, published August 15, 2017, asks whether crowdsourcing can improve Internet of Things security. Editor Curt Franklin hosts Bugcrowd CEO Casey Ellis to explore why IoT security differs from enterprise security and how professionals can make IoT bugs easier to find.
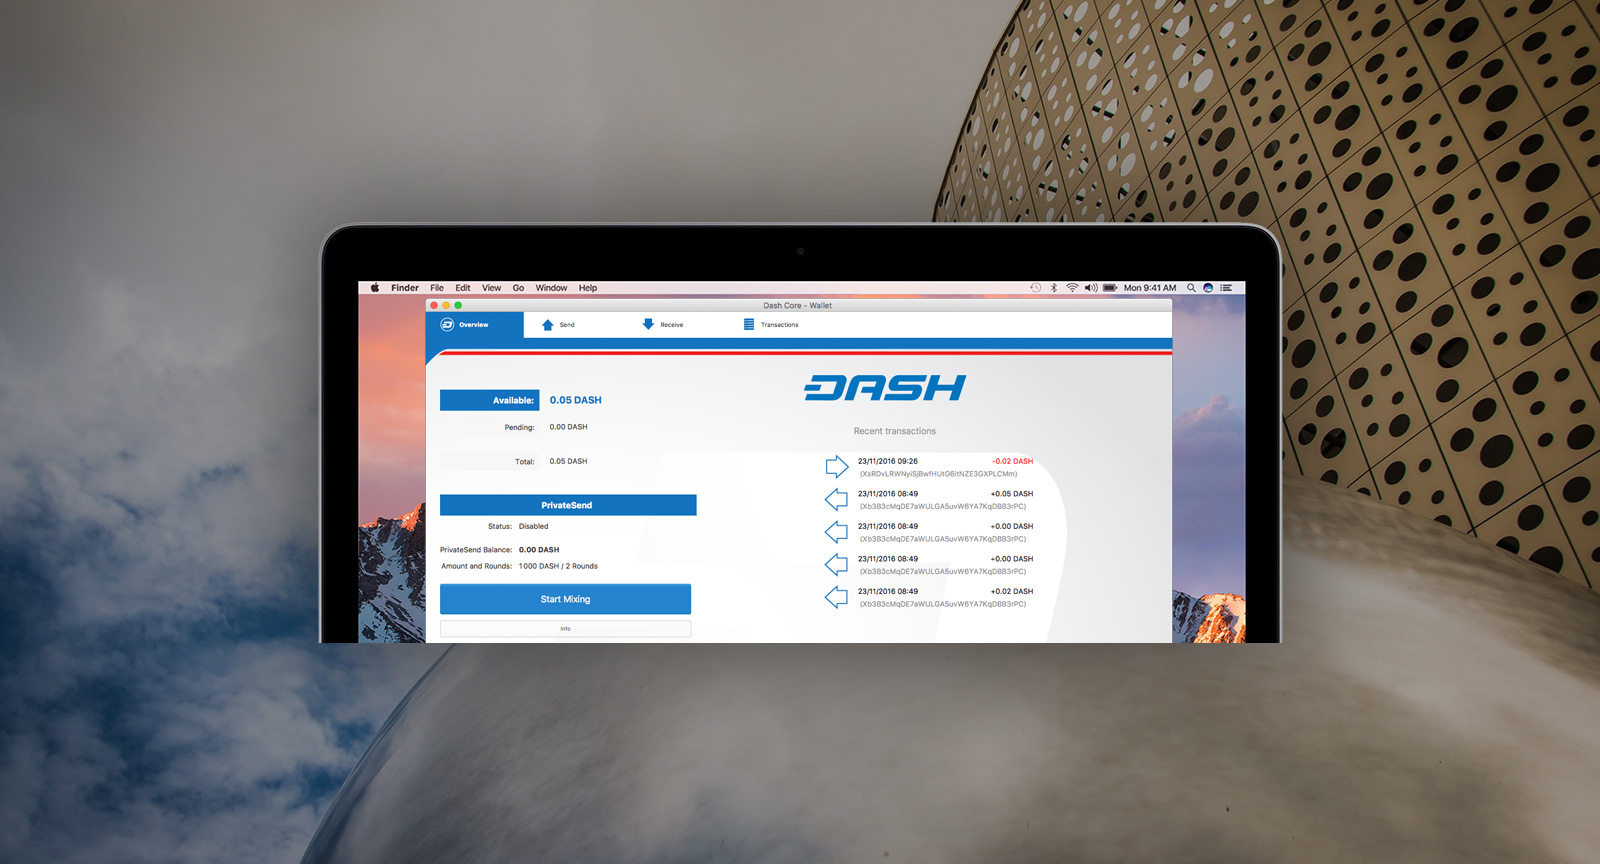
Dash invites researchers to hack their blockchain - Help Net Security
Help Net Security published this 2017 article about the Dash bug bounty, run through Bugcrowd to have researchers find critical software vulnerabilities. Bugcrowd CEO Casey Ellis says a shortage of cybersecurity professionals and an expanding attack surface leave companies at a disadvantage, and self-managed programs quickly overwhelm them.

Dash employs cybersecurity service Bugcrowd to identify blockchain vulnerabilities
Dash cryptocurrency engaged Bugcrowd's cybersecurity services to identify vulnerabilities in its blockchain infrastructure, according to EconoTimes. Casey Ellis, Bugcrowd's founder and CEO, supported the partnership to help strengthen Dash's security posture through crowdsourced vulnerability research.

13-year-old Pakistani hacker finds bugs at world’s top tech companies
An article published in Republica profiles a 13-year-old Pakistani hacker who discovered and reported security vulnerabilities at major technology companies. Casey Ellis is mentioned as a figure supporting young security researchers and encouraging responsible vulnerability disclosure practices globally.

WikiLeaks Dumps Alleged CIA Malware and Hacking Trove
BankInfoSecurity published an article on the security implications for financial institutions following WikiLeaks' release of alleged CIA hacking tools and malware. Casey Ellis provided analysis on the incident's impact and what organizations should prioritize in response to the disclosure.

WikiLeaks Dumps Alleged CIA Malware and Hacking Trove
DataBreachToday published an article on the security implications of WikiLeaks' release of alleged CIA hacking tools and malware for the financial industry. Casey Ellis commented on the risks these disclosed vulnerabilities and tactics pose to financial institutions' security posture and defense strategies.

WikiLeaks Dumps Alleged CIA Malware and Hacking Trove
Government Info Security covered the WikiLeaks release of alleged CIA malware and hacking tools in August 2017. Casey Ellis provided analysis on the security implications and fallout from the disclosure of the agency's cyber capabilities.

WikiLeaks Dumps Docs on CIA’s Hacking Tools
KrebsOnSecurity reported on the WikiLeaks release of documents alleging CIA hacking tools and their capabilities. Casey Ellis provided analysis on the disclosed tools' implications for cybersecurity defenses and vulnerability disclosure practices.

CIA hacking dossier leak reignites debate over vulnerability disclosure
The Register published an analysis of the vulnerability disclosure debate sparked by WikiLeaks' release of alleged CIA hacking tools in March 2017. Casey Ellis contributed perspective on responsible disclosure practices and the tension between security researchers, vendors, and government agencies in managing software vulnerabilities.

WikiLeaks Dumps Alleged CIA Malware and Hacking Trove
CUInfoSecurity published an analysis of WikiLeaks' release of alleged CIA hacking tools and malware in August 2017. Casey Ellis commented on the security implications of the disclosed exploit code and its impact on defenders across the industry.

Overnight Cybersecurity: Hackers breach voting machines | Kelly's move to White House leaves void at DHS | House panel presses agencies for info on Russian cyber firm
This Overnight Cybersecurity newsletter from The Hill, published July 31, 2017, rounds up daily hacking and data privacy news, including reports on hackers breaching voting machines. Casey Ellis, founder of Bugcrowd, is quoted saying automotive is the fastest growing bug bounty sector as automakers struggle to hire the specialized researchers they need.

Demand for automotive cybersecurity pros outpaces supply
A 2017 article in The Hill examines the shortage of automotive cybersecurity professionals relative to industry demand. Casey Ellis discusses the talent gap and the need for organizations to develop skilled security personnel in the automotive sector.

Election tech hacked within hours at DEF CON Voting Village
A July 2017 SC Magazine article covers the DEF CON Voting Village, where election technology was compromised in hours by security researchers. Casey Ellis participated in the event, demonstrating vulnerabilities in voting systems and highlighting the need for stronger security measures in election infrastructure.

Expert Panel: Bug Bounty Trends and What They Mean
BrightTalk hosted an expert panel discussion on bug bounty trends and their implications in July 2017. Casey Ellis participated on the panel to discuss developments and insights in the bug bounty space.

LaunchVic, Startmate to deliver free workshops
LaunchVic and Startmate announced a series of free workshops for aspiring entrepreneurs, according to The Australian. Casey Ellis participated in the initiative to support early-stage startup development in the Australian entrepreneurial ecosystem.

Melbourne accelerator programme seeks APAC cybersecurity startups
CyRise, a Melbourne-based accelerator program, announced a call for cybersecurity startups across the APAC region to apply for funding and support. Casey Ellis served as an adviser and backer of the initiative aimed at developing early-stage security companies in the Asia-Pacific market.

CyRise set to fast-track Australian cyber security startups
Smart Company reported on the launch of CyRise, an accelerator program designed to fast-track growth of Australian cybersecurity startups. Casey Ellis served as a founding advisor to the program, bringing expertise in supporting early-stage security ventures.

The State of Bug Bounties & Ask Me Anything
Bugcrowd LevelUp0x01 published a stage presentation titled "The State of Bug Bounties & Ask Me Anything" in July 2017. Casey Ellis discusses the current landscape of bug bounty programs and answers audience questions about trends and developments in the field.

Why Offering Bug Bounties Will Be Widespread, Even in Government
Government Technology published an opinion piece in 2017 on the expansion of bug bounty programs into government agencies as standard practice. Casey Ellis discusses why organizations across sectors, including government, will increasingly adopt bug bounties to identify and address security vulnerabilities.

Dimension Data-backed program CyRise searches for cyber security startups
CRN Australia reported on the CyRise accelerator program, backed by Dimension Data, as it sought promising cybersecurity startups for its inaugural cohort. Casey Ellis served as a mentor and advisor to the program, helping early-stage founders develop their security ventures and business strategies.