

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
Unusual Gathering Episode XIV: The ITSP Magazine Online Holiday Party
ITSPmagazine published Episode XIV of Unusual Gathering, a holiday special podcast episode featuring industry figures discussing the year in cybersecurity. Casey Ellis participated in the festive discussion alongside other guests on the show.
Cybersecurity Research Reveals IoT Vulnerabilities, Nation-State Threats
A December 2018 cybersecurity research roundup from eSecurity Planet covers IoT vulnerabilities and nation-state threats. The article includes insights and data from Bugcrowd on emerging security challenges identified through vulnerability research and crowdsourced security testing.
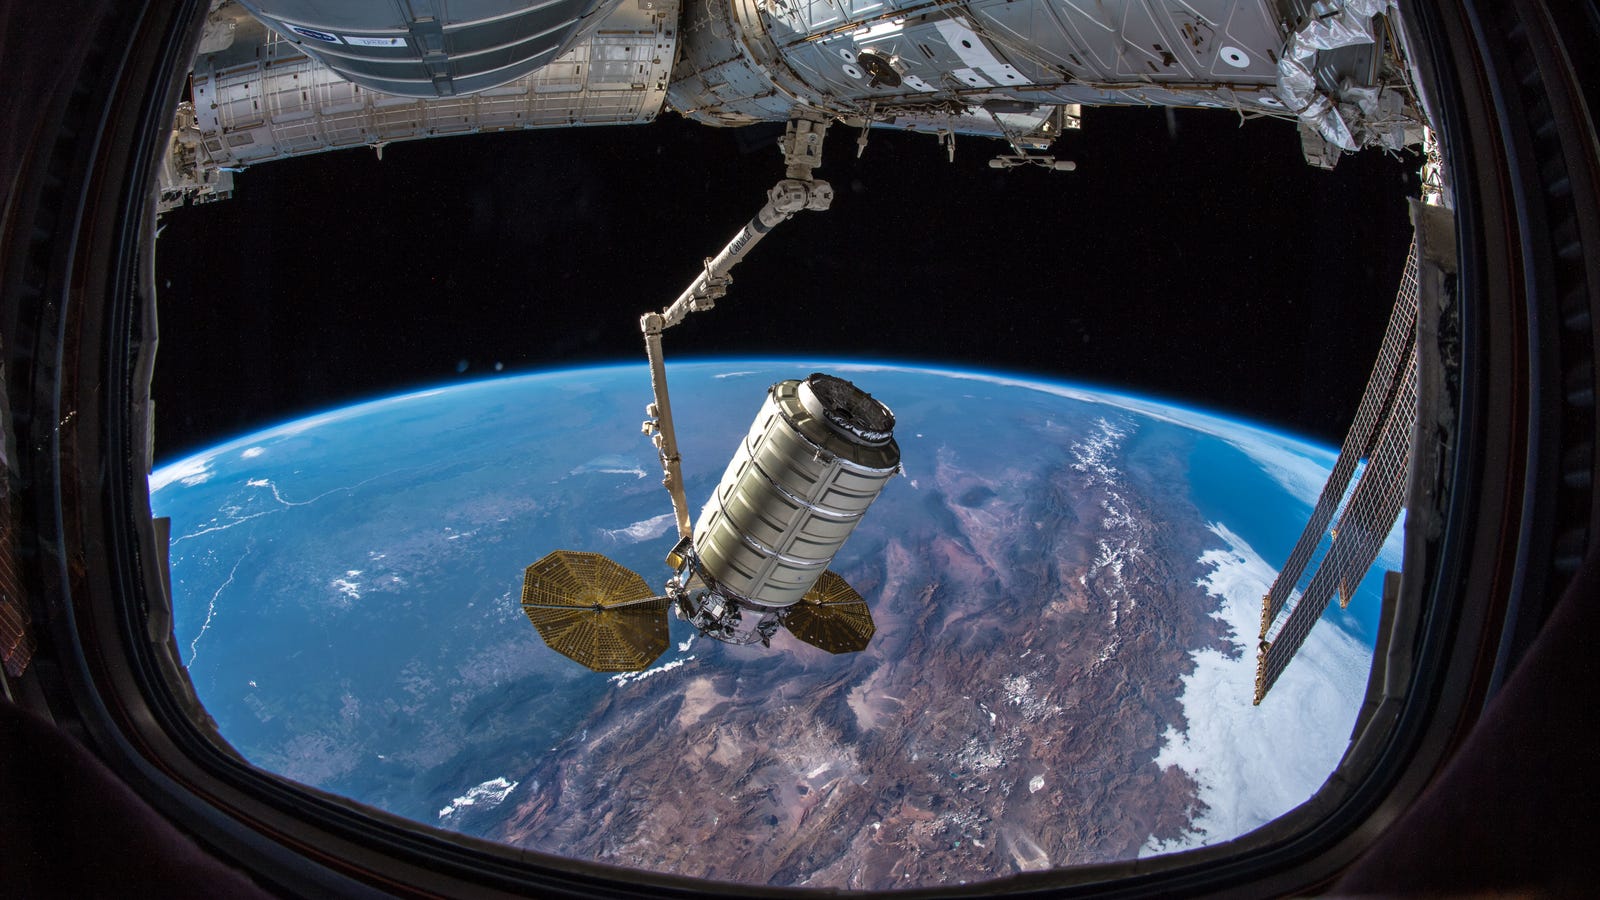
NEWS INSIGHTS: SOMEONE HACKED NASA
A December 2018 article in the Journal of Cyber Policy covered a data breach at NASA. Casey Ellis provided commentary on the incident and discussed its broader implications for the organization.
Future Job: Corporate Bug Hunting
CDOTrends published an article in December 2018 examining corporate bug hunting as an emerging career path. Casey Ellis provided insights on the expansion of the bug bounty industry and its role in creating new employment opportunities.
OSS Security a Top Priority in National Cyber Strategy
A Security Boulevard article examines the prioritization of open-source software security within U.S. national cyber strategy. Casey Ellis provides analysis on how OSS security has become a key focus area in broader cybersecurity policy and infrastructure protection efforts.
Bug Hunting is Cybersecuritys Skill of the Future
Infosecurity Magazine published an article discussing bug hunting as an emerging core competency within the cybersecurity industry. Casey Ellis contributed commentary on the growing importance of bug hunting practices in the sector.
Some freelance hackers can get paid $500,000 a year to test the defenses of companies like Tesla
NBC News published a feature on the earning potential of freelance hackers who participate in bug bounty programs. Casey Ellis discusses how the economics of these programs work and what drives compensation levels for security researchers testing corporate defenses.
Some freelance hackers can get paid $500,000 a year to test defenses of companies like Tesla
CNBC published an article examining how freelance ethical hackers can earn up to $500,000 annually by testing corporate security defenses through bug bounty programs. Casey Ellis discusses the financial rewards available to top performers in the coordinated vulnerability disclosure space.
The rockstar hackers protecting you from the bad guys
CNET published a feature article in December 2018 profiling ethical hackers who work to protect companies and consumers from cyber threats. Casey Ellis was included among the security researchers recognized for their contributions to identifying and mitigating vulnerabilities in digital systems.
Bounty Hunters, Bugcrowd, The End of Penetration Testing, and Crowd Sourced Vulnerability Research
LeetSpeak podcast episode from December 2018 featured Casey Ellis discussing bug bounty programs and their impact on vulnerability research practices. Ellis argued that crowdsourced security approaches are fundamentally reshaping how organizations discover and address software vulnerabilities compared to traditional penetration testing methods.
Bug Bounty as a tool towards a Vulnerability Management Program (12ENISE)
A 2018 presentation at 12ENISE conference on YouTube covers Casey Ellis's approach to integrating bug bounty programs into organizational vulnerability management strategy. Ellis discusses how bug bounty functions as a tactical tool within a broader vulnerability management program rather than as a standalone initiative.
Hacker Steals Crypto from Copay Wallets Apps
A Infosecurity Magazine article from November 2018 reports on a security incident in which a hacker stole cryptocurrency from Copay wallet users by compromising a third-party code library. Casey Ellis commented on the incident and its implications for supply chain security in wallet applications and cryptocurrency platforms.
Hacker takes over JavaScript library, injects malware to steal Bitcoin
SC Magazine reported on a supply chain attack in which a hacker compromised a popular JavaScript library and injected malicious code designed to steal cryptocurrency. Casey Ellis commented on the incident's implications for software security and the risks posed by compromised dependencies in the development supply chain.
Cryptocurrency-Stealing Code Distributed via Popular Library
SecurityWeek reported on a supply chain attack in which cryptocurrency-stealing code was distributed through a popular code library. Casey Ellis discussed the incident's implications for software supply chain security and the risks posed by compromised dependencies to developers and users.
The Future of Safe Harbor Is Now
Forbes published an article by Casey Ellis on safe harbor protections for ethical hackers. Ellis argues that establishing clear safe harbor rules is essential to encourage responsible security research and protect researchers from legal liability.
Getting A Return On Your Information Security Investment
ITSPmagazine Podcast published an episode on measuring and articulating the return on investment of security programs. Casey Ellis discusses with Elizabeth Wharton how organizations can demonstrate and quantify the value their security initiatives deliver.
“Understand How To Scale” 5 Leadership Lessons With Casey Ellis
An article published by Thrive Global presents five leadership lessons on scaling a business drawn from an interview with Casey Ellis. Ellis discusses practical approaches to organizational growth and building teams capable of managing expansion.
US Department of Defense Expands Bug Bounty Efforts
eWEEK reported on the U.S. Department of Defense's expansion of bug bounty programs to cover additional systems and assets. Casey Ellis was cited for his work advancing coordinated vulnerability disclosure practices that informed the department's security initiatives.
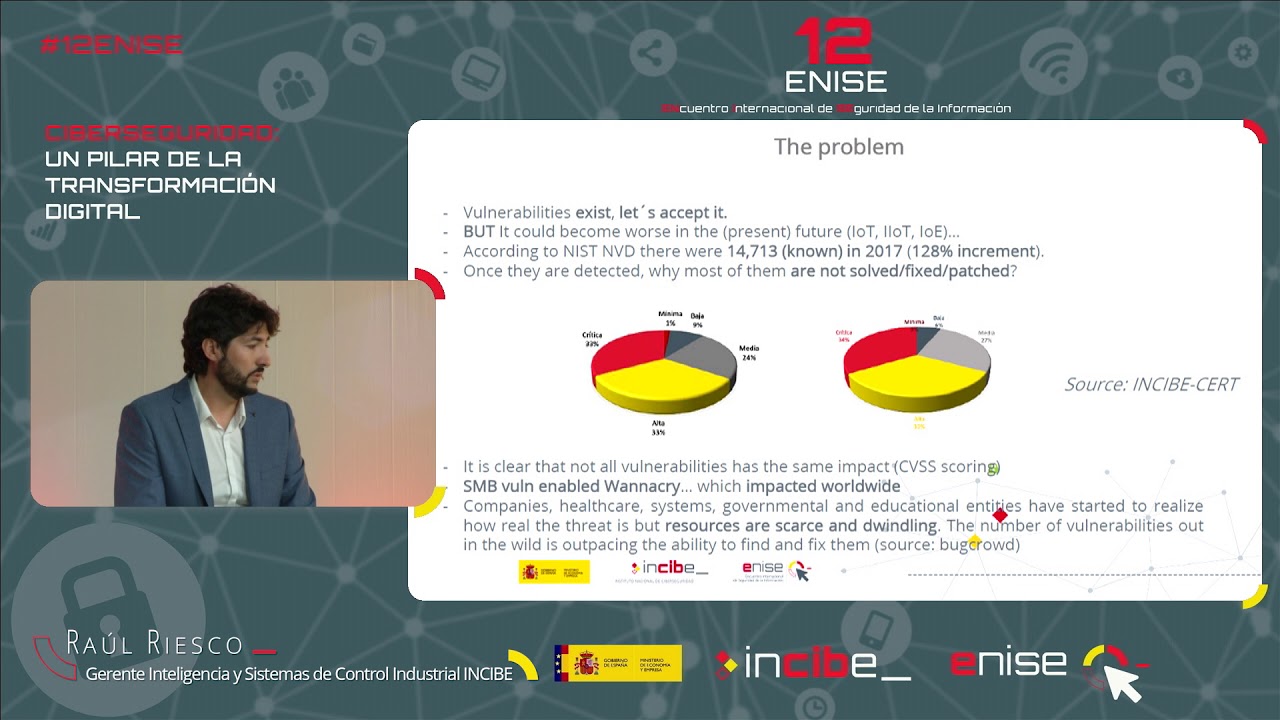
Bug Bounty as a tool towards a Vulnerability Management Program
A video presentation at the 2018 ENISA Summit explores bug bounty programs as a component of broader vulnerability management. Casey Ellis discusses how organizations can integrate bug bounty initiatives into their security strategy to identify and address vulnerabilities systematically.
Halt, who goes there? Identity access management
SC Magazine published an in-depth article on the challenges and solutions in identity and access management. Casey Ellis discusses IAM approaches and best practices for securing identity infrastructure in modern enterprise environments.
The Cybersecurity 202: Lawmakers are ready to embrace ethical hackers, even if DHS isnt
A Washington Post Cybersecurity 202 column from September 2018 examines legislative momentum behind ethical hacking programs despite resistance from some federal agencies. Casey Ellis is cited as a key voice advocating for formal bug bounty and vulnerability disclosure frameworks that benefit both security researchers and government cybersecurity efforts.
Facebook Now Offers Bounties For Access Token Exposure
Threatpost reported on Facebook's expansion of its bug bounty program to reward researchers for discovering exposed user access tokens. Casey Ellis contributed insight on the significance of this program expansion for incentivizing the discovery and responsible disclosure of critical authentication vulnerabilities.
Risk & Repeat: Can Disclose.io help protect vulnerability researchers?
A TechTarget podcast from September 2018 examines whether the disclose.io framework can protect vulnerability researchers from legal threats. Casey Ellis discusses how the framework addresses legal risks researchers face when disclosing security vulnerabilities to organizations.
Tesla offers 'goodwill' to security researchers hacking its cars
This CyberScoop article from September 6, 2018, covers Tesla's vulnerability disclosure page, which says the company values security researchers' work. Casey Ellis, founder of BugCrowd, called the move a massive step forward in reducing risk for vulnerability disclosure and bug bounties, and said he hopes it becomes the standard.
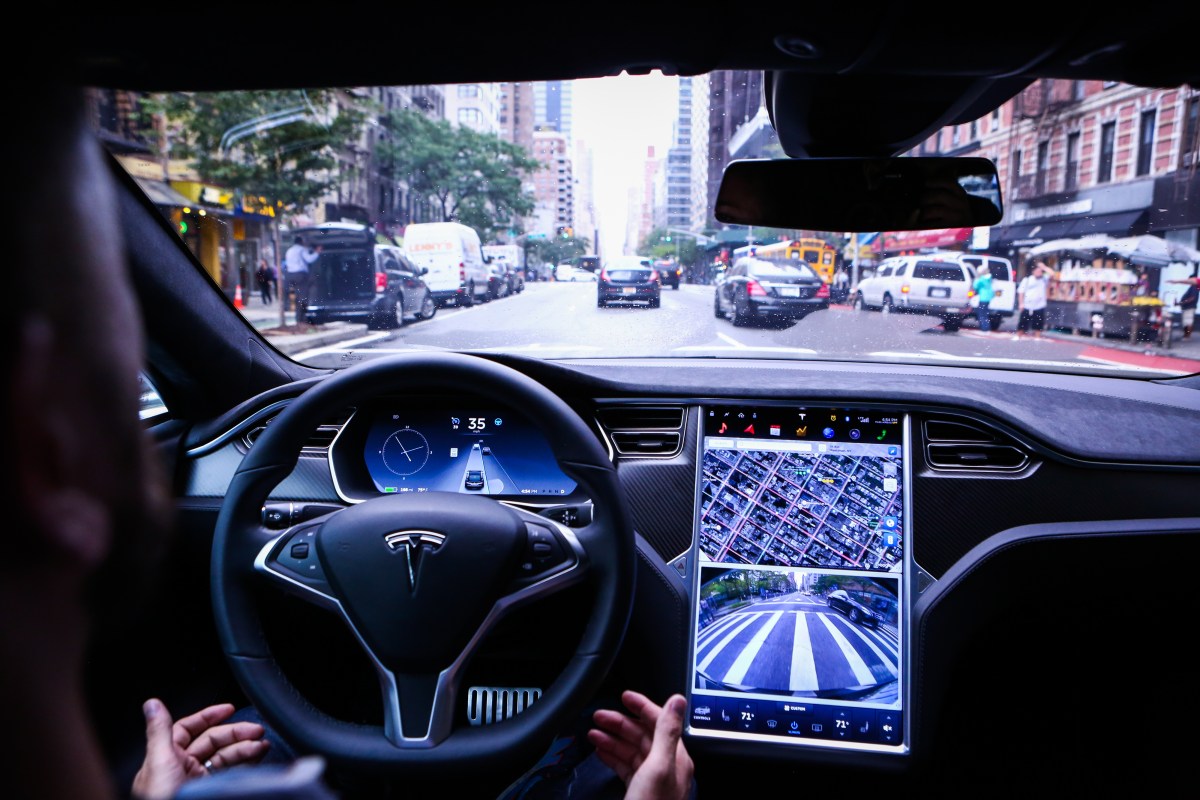
Tesla’s new bug bounty protects hackers — and your warranty
TechCrunch reported on Tesla's updated bug bounty policy, which grants legal protections and warranty safeguards to security researchers who responsibly disclose vulnerabilities. Casey Ellis contributed commentary on the importance of the policy in encouraging responsible disclosure and protecting researchers from legal liability.
NIST issues guidance for protecting medical IoT devices
NIST released guidance for securing medical Internet of Things devices, as covered by SC Magazine. Casey Ellis commented on the importance of protecting medical IoT devices as a critical security priority.
Hackers for hire
Long Island Business News published a feature on the "hackers for hire" industry and the business models behind ethical hacking and bug bounty programs. Casey Ellis explains how security researchers and companies are creating marketplaces that connect hackers with organizations seeking to improve their defenses.
Bounties Mount for Bugs
Communications of the ACM published an article examining the growing value and prevalence of bug bounty programs across the software industry. The piece discusses how security researchers and companies are increasingly using bounties as a mechanism to identify and remediate vulnerabilities in production systems.
Crowdsourcing the hunt for software bugs is a booming business—and a risky one
MIT Technology Review published an analysis of the crowdsourced bug-hunting industry, examining both its growth and associated risks. Casey Ellis discusses the benefits and challenges of platforms that coordinate security researchers to identify software vulnerabilities at scale.
The Threatpost Podcast: Bugcrowd Founder on Profitable Bounty Programs
The Threatpost Podcast featured Casey Ellis in an August 2018 episode to discuss bug bounty program management. Ellis addressed the factors that make bounty programs financially sustainable and mutually beneficial for organizations and participating security researchers.