

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
Australian Gov't Weighs Mandatory AI Incident Reporting
This Dark Reading article reports that Australia's government is weighing mandatory AI incident reporting for frontier AI companies after an agentic attack on its own systems. Casey Ellis, founder of disclose.io and Bugcrowd, describes public anger over the delayed notification and argues AI agents operating outside authorized scope should be reportable by default.
Google Is Pausing a Lucrative Bounty Hunter Program. The Reason Points to a Weakness With Using AI
This Inc. article by Chloe Aiello reports that Google temporarily paused its open-source software vulnerability reward program because of a rise in automated submissions. Bugcrowd founder Casey Ellis told TechCrunch that AI has not yet caused a significant spike in low-quality slop reports, though overall submission volume at Bugcrowd has jumped.
AI Just Broke Vulnerability Management
Resilient Cyber published this October 3, 2026 article, AI Just Broke Vulnerability Management, analyzing published results from Glasswing and Patch the Planet and what their fix rates mean for enterprise backlogs. The author credits Casey Ellis with a line quoted in the piece: the volume apocalypse was already here, just unevenly distributed.
The Founder Who Convinced Google to Let 10,000 Hackers Attack It | Casey Ellis
This broadcast interview, The Founder Who Convinced Google to Let 10,000 Hackers Attack It, was published on YouTube by The Hacking Games. Casey Ellis appears as the featured guest, the founder of Bugcrowd, speaking with host Fergus Hay about how major companies came to invite outside hackers to test their systems.
Build the Tooling, Don't Be the Tooling
This Field Note stage session at [un]prompted.au 2026 is scheduled for September 19, 2026, in the Main Hall. Casey Ellis of Tall Poppy Group and disclose.io argues people should build tooling rather than be the tooling, using AI to create self-improving systems, such as a security tool that gets better each time it fails.
Episode 45: AI & Bug Bounties with Casey John Ellis!
Episode 45 of the Across the Pondcast cybersecurity podcast, published September 18, 2026, is titled "AI Bug Bounties with Casey John Ellis" and is hosted by Tib3rius and Andy Swift. Casey joins the hosts as a guest to discuss bug bounty and other topics in the era of AI.
Black Hat 2026: Why Threat Researchers Are Hoarding Zero-Days
This AI Security Podcast episode, released September 15, 2026, is a broadcast interview hosted by Ashish Rajan. Casey Ellis, founder of Bugcrowd and pioneer of Disclose.io, calls the flood of low-quality, noisy vulnerability submissions a slopdemic rather than a vulnpocalypse, and discusses why skilled researchers are hoarding zero-days.
The Remediation Receipts
The Remediation Receipts, a Resilient Cyber piece from September 14, 2026, examines what Project Glasswing and Patch the Planet reveal about the patching burden enterprises inherit. The author credits Casey Ellis with the observation that the vulnpocalypse was already here but unevenly distributed, a point the piece uses to frame teams drowning in backlogs.
The “Left” in Shift-Left Moved
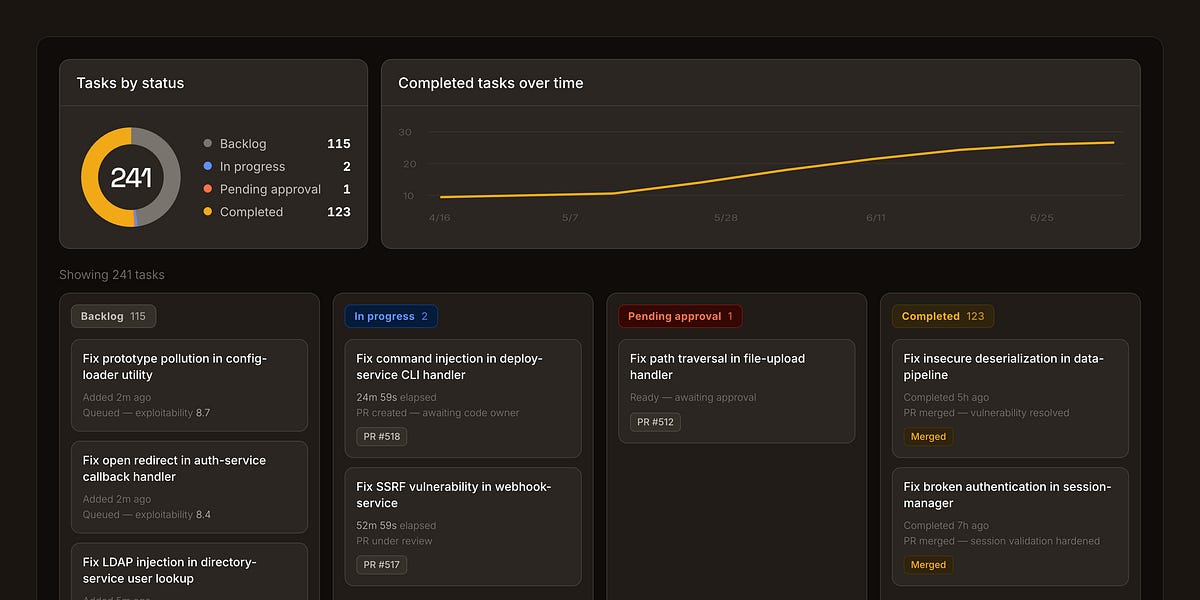
This Resilient Cyber newsletter post, published September 10, 2026, examines how AI is reshaping application security, including code now written by agents on developer workstations. In a July interview on the author's show, Casey says AI collapsed the cost of finding and reporting vulnerabilities, raising signal and noise roughly tenfold.
The Vulnerability Nobody Meant to Find: How is AI-enabled Vulnerability Discovery Changing Our Understanding of Cyber Harm?
This interview, published by Geneva Dialogue, features Casey Ellis, founder of Bugcrowd and The disclose.io Project, in conversation with Anastasiya Kazakova of DiploFoundation. Ellis examines how AI systems that find and sometimes choose vulnerabilities faster than humans can respond challenge coordinated disclosure, defender-offender parity, and state and private sector responsibility.
AI Will End the Era of Hidden Vulnerabilities. Are Vendors Ready?
A Dark Reading article from September 4, 2026, examines how AI-accelerated bug discovery is straining software vendors' remediation and disclosure systems. Casey Ellis, co-founder of Disclose.io and former Bugcrowd founder, argues that many organizations lack clear reporting channels and safe harbors for good-faith researchers, and calls treating them as criminals a mistake.
The Vulnpocalypse Is Repricing the Bug Bounty Economy
This Dark Reading article by Alexander Culafi, published August 28, 2026, examines how AI-powered vulnerability reports are lowering bug bounty prices. Casey Ellis, president and co-founder of Disclose.io and founder of Bugcrowd, says the bug bounty ecosystem is not static and that today's middle class could look very different as the current storm passes.

I'm Not AGI Pilled. I'm Human Pilled - with Casey Ellis
This broadcast episode from the ZeroSum Podcast, published on YouTube on August 18, 2026, is a video program in the show's series. Casey Ellis appears as a guest on the episode, where he takes part in the conversation alongside the show's host and shares his perspective.
Sponsored: What npm 12 fixes… and what it doesn’t
This sponsored podcast episode from Risky Business Media, published August 17, 2026, examines npm 12's move to disable install scripts by default. Casey Ellis, Bugcrowd founder, chats with Socket founder Feross Aboukhadijeh, who explains why teams need to understand third-party package source code as attackers shift payloads into it.
Uncle Sam Seeks Private Hackers to Disrupt Criminal Networks
This BankInfoSecurity article reports that the White House has launched a program engaging private cybersecurity firms, with guidelines that explicitly authorize accessing systems without owner or operator authorization. Casey Ellis, founder of Bugcrowd, notes in a LinkedIn post that this wording paraphrases the Computer Fraud and Abuse Act, which prohibits such access.
SLOP ROULETTE at SLOPCON 2026
SLOP ROULETTE is a stage session listed in the SLOPCON 2026 archive, published by SLOPCON, held overnight on 7-8 August 2026 in Room W222 at DEF CON 34 in Las Vegas. Casey presented the 00:15 slot under the conference theme "AI Generated, Human Presented," as part of the overnight program.
Filibuffer Overflow: Hackers Stage a Congressional Hearing
This stage session from DEF CON 34, published by the DEF CON 34 program, is a staged hearing titled Filibuffer Overflow, held in the Policy Village on 7 August 2026. Casey takes the stage as a mock Congressional testimony witness in a format the group previously ran in a real Senate hearing room.
Slopdemic, Not Vulnpocalypse (Yet)
This Resilient Cyber podcast episode, published July 30, 2026, features an interview by Chris Hughes with Bugcrowd founder and disclose.io co-founder Casey Ellis. Ellis discusses what AI is doing to vulnerability discovery, bug bounties, open source, and security research policy, including how the cost of finding and reporting vulnerabilities has shifted.
Sponsored: Thinkst on building companies that don’t suck
A sponsored interview segment from Risky Business Media features Casey Ellis discussing company culture and customer relations with Haroon Meer of Thinkst. Ellis and Meer explore principles for building organizations that maintain positive relationships with their customer base rather than generating frustration or dissatisfaction.
Gold Eagle Clearinghouse Targets Security Gap, but How Is Unclear
Dark Reading published an article on Gold Eagle Clearinghouse's exploitation of security gaps in financial systems. Casey Ellis is quoted discussing the vulnerabilities involved and their broader implications for sector-wide security practices.
Casey Ellis on How AI Is Reshaping Vulnerability Research and Patching
An episode of the Microsoft Threat Intelligence Podcast features Casey Ellis discussing how artificial intelligence is transforming vulnerability research, bug bounty programs, and cyber defense strategies. Ellis addresses the expanding volume of vulnerabilities, responsible disclosure challenges, AI-assisted attacks, and the implications of advanced tools for both defenders and attackers.

Security Community Slams US Ban on Exporting Mythos, Fable
This Dark Reading article, from June 16, 2026, reports on an open letter urging the US government to lift export controls on Anthropic's Claude Fable 5 and Mythos 5 models. Casey Ellis co-signed the letter, which argues the restriction would only help US competitors and the cited research can be replicated elsewhere.

Cybersecurity vets protest 'dangerous' US government ban on Anthropic's most powerful models
A TechCrunch article covers cybersecurity experts' objection to US government export controls on Anthropic's advanced AI models. Casey Ellis joined dozens of security professionals in urging the White House to lift restrictions, contending the ban undermines defenders' ability to secure software and products.
Will AI Kill the Bug Bounty Industry?
SecurityWeek's article Will AI Kill the Bug Bounty Industry? examines how Anthropic's Mythos model is accelerating vulnerability discovery and forcing bug bounty platforms and offensive security teams to adapt. The piece also credits Casey Ellis as co-founder of Bugcrowd, one of four primary bounty platforms established in 2012.
Microsoft says it won't go after security researchers after the internet called them out
Microsoft announced it will not pursue legal action against security researchers following public criticism, according to Windows Central. Casey Ellis contributed to the discussion around responsible disclosure practices and the importance of constructive collaboration between software vendors and the security research community.

Smashing the (Policy) Stack for Public Safety & (Not) Profit?!
Josh Corman and Casey John Ellis presented a NaClCON session examining cybersecurity policy, public safety, and public-interest work.

Sponsored: Inside CISA's disastrous secrets leak
Risky Business Media published a sponsored interview segment in which Casey Ellis discusses the recent CISA secrets leak with Truffle Security founder and CEO Dylan Ayrey. Ellis examines the incident's implications and security lessons relevant to the vulnerability disclosure and cybersecurity community.

Microsoft's Zero-Day Legal Threats Spark Backlash
Dark Reading published an article examining legal threats and industry backlash following a Microsoft zero-day vulnerability disclosure. Casey Ellis commented on the broader implications of how security researchers and coordinated disclosure practices navigate legal risks and responsible vulnerability reporting in the current threat landscape.
Vulnerability disclosure with Casey Ellis
Casey Ellis joined Open Source Security to discuss the persistent challenges of vulnerability disclosure and the additional pressure created by AI-generated findings.

20 Leaders Who Built the CISO Era: 2 Decades of Change
This Dark Reading feature, published May 12, 2026, profiles 20 leaders who shaped the CISO era, including CISOs, founders, researchers, and policymakers. Casey Ellis, founder of Bugcrowd, praises Katie Moussouris for pioneering vulnerability disclosure and says they have worked together in bug bounty for nearly 13 years.