

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.

2021 marks another record year for security vulnerabilities
TechRepublic published an article examining the record number of security vulnerabilities disclosed in 2021. Casey Ellis provides insight into the factors driving the surge in vulnerability disclosures and their implications for the security industry.

With 18,378 vulnerabilities reported in 2021, NIST records fifth straight year of record numbers
ZDNet published a report on NIST data showing that 2021 saw 18,378 vulnerabilities discovered, continuing a fifth consecutive year of record numbers. Casey Ellis commented on the vulnerability landscape and the implications of sustained increases in reported security flaws.

How to get started with bug bounties and finding vulnerabilities | Cyber Work Podcast
A Cyberwire podcast episode from December 2021 features Casey Ellis discussing how to begin participation in bug bounty programs and the process of identifying vulnerabilities. Ellis provides guidance on entry points for security researchers interested in coordinated vulnerability disclosure and bug bounty participation.

AT&T Looks to Shut Down Botnet that Attacked 5,700 Network Appliances
eSecurity Planet reported on AT&T's efforts to shut down the EwDoor botnet, which compromised over 5,700 carrier-grade network address translation devices. Casey Ellis commented on the incident's significance for critical infrastructure security and the importance of coordinated response efforts against emerging botnet threats.

Arrest Points to Ubiquiti Breach Being an Inside Job
BankInfoSecurity reported on the arrest of a former Ubiquiti employee charged with orchestrating a data breach and extortion attempt against the networking company. Casey Ellis commented on the incident's implications for corporate security practices and insider threat detection.

Searching for Bugs in Open Source Code
Security Boulevard published an article on the challenges and importance of proactively identifying and fixing security vulnerabilities in open-source software. Casey Ellis discusses the need for systematic approaches to vulnerability discovery and remediation in open-source projects.

300,000 banking Trojan infections from Google Play in 4 months
Security Magazine reported on a wave of banking trojan infections from malicious apps on Google Play that resulted in over 300,000 infections across four months. Casey Ellis contributed analysis on the threat landscape and the security implications of malware distribution through official app marketplaces.

CTO Talk: Q&A with Bugcrowd’s Casey Ellis
Verdict published a Q&A interview with Casey Ellis, founder and CTO of Bugcrowd, in November 2021. Ellis discusses how cybersecurity has evolved and explains the role crowdsourced security plays in modern defense strategies.

Q&A: Casey Ellis
A Q&A session published by Duo Security explores Casey Ellis's perspectives on bug bounties and vulnerability disclosure practices. Ellis discusses the evolution of bug bounty programs and shares insights on the future direction of how organizations discover and address security vulnerabilities.

Decipher Podcast: Casey Ellis
Decipher Security Podcast published an episode featuring Casey Ellis on November 23, 2021. Ellis discusses how vulnerability disclosure programs have evolved, gained adoption, and become standardized in the United States and internationally.

Malicious Golang program attacks e-commerce servers
A report from SC Magazine details malicious Golang malware targeting e-commerce servers to steal payment information. Casey Ellis provided analysis on the threat's implications for retail infrastructure and payment security vulnerabilities.

Digital Bounty Hunters Want To Help Businesses Track Down
A Forbes article examines the emerging practice of applying bug bounty models to identify bias and discrimination in artificial intelligence systems. Casey Ellis discusses how crowdsourced security approaches can be adapted to surface algorithmic fairness issues before they cause harm to users and organizations.

Ethical Hackers Prevented $27B in Cybercrime
The Security Boulevard article "Ethical Hackers Prevented $27B in Cybercrime," published November 17, 2021, examines how security researchers skew younger, are more entrepreneurial, and span generations. Casey Ellis, founder and CTO of Bugcrowd, comments that 79% of ethical hackers taught themselves using online resources and calls the cohort's impact on thwarting cyberattacks monumental.

U.S. Government Details Federal Agency Incident Response
Duo Security published an analysis of new U.S. government directives establishing incident response requirements for federal civilian agencies. Casey Ellis is quoted discussing the practical implications of the government's clearer cybersecurity incident playbooks and their effect on federal agency preparedness.

Ethical Hackers Stymie $27bn of Cybercrime
A report in InfoSecurity Magazine details research estimating that ethical hackers prevented over $27 billion in cybercrime damages during a one-year period. Casey Ellis contributed to the research, which quantifies the financial impact of vulnerability disclosure and coordinated security research on reducing criminal losses.

Midsize Companies Still Struggle with Security
This Security Boulevard article from November 2021, titled "Midsize Companies Still Struggle with Security," examines cybersecurity challenges facing midsize organizations. Casey Ellis, founder and CTO of Bugcrowd, says the main midmarket weaknesses are attack surface drift, patch management, and application security, and suggests vulnerability disclosure programs to address them.
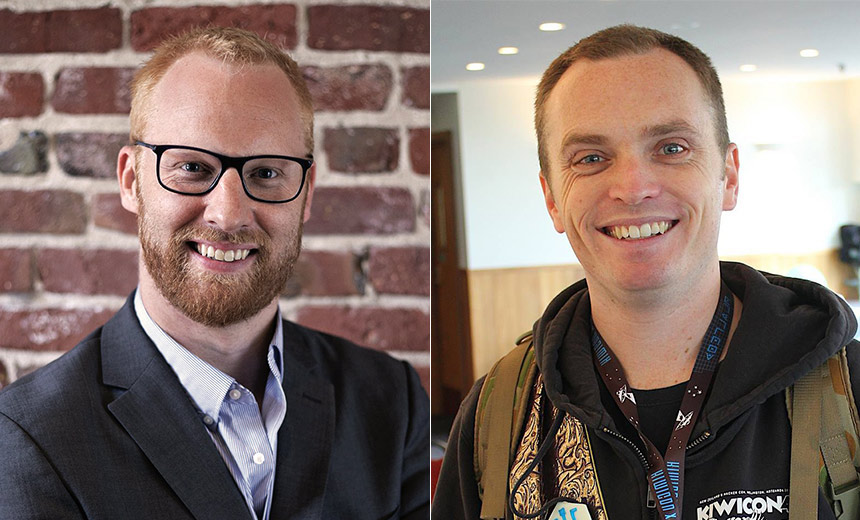
Why Reporting Security Bugs Can Be Fraught With Tension
This 2021 video interview from BankInfoSecurity examines the tensions researchers face when reporting vulnerabilities to organizations without disclosure policies. Casey Ellis, founder, CTO and chairman of Bugcrowd, says legal protections are needed for responsible researchers, who function as the internet's immune system, and he is involved with Disclose.io, a safe harbor initiative.
Patching Process Remains a Security Bottleneck
This October 2021 Security Boulevard article, Patching Process Remains a Security Bottleneck, covers why patching stays slow and complex. Casey Ellis, founder and CTO of Bugcrowd, calls patch management one of the unavoidable chores of IT management and says failures usually stem from incomplete asset inventories.
Cyber-security threat hunters seek legal protections
Published by The Register on October 11, 2021, this article reports on efforts by the Cybersecurity Advisors Network to secure legal protections for cyber-security threat hunters. Casey Ellis, founder, chair, and CTO of Bugcrowd, is among the figures who endorse the network's efforts, alongside Katie Moussouris and Ciaran Martin.

Cybersecurity Awareness Month with Casey Ellis, CTO, Bugcrowd and Beau Woods, Senior Advisor, CISA
The CyberWire published a video segment featuring Casey Ellis, CTO of Bugcrowd, and Beau Woods, Senior Advisor at CISA, discussing cybersecurity awareness during October 2021. Ellis and Woods explored implications of recent security incidents for security leaders and organizational defense strategies.
Compliance and "The Crowd", Part 1 - Casey Ellis - SCW #88
Compliance and "The Crowd", Part 1 is a video podcast episode from Security and Compliance Weekly, released September 28, 2021 as episode 88. In it, Casey joins Jeff to examine how crowdsourced and multi-sourced risk assurance approaches hold up when measured against established security compliance standards.
Compliance and “The Crowd”, Part 2 – Casey Ellis – SCW #88
This podcast segment, released September 28, 2021, is Part 2 of Compliance and The Crowd from episode 88 of Security Weekly, published by SC Media. Casey Ellis appears as a guest in the segment, which explores how crowd-based security approaches fit within broader security compliance work.

Consumer Cyber Stress Requires Focus on Security
This Security Boulevard article from September 27, 2021, examines rising consumer cybersecurity stress and how organizations can respond to it. Casey Ellis, founder and CTO of Bugcrowd, says consumer stress has become a political issue that is not going away, and he argues that product makers should make risky decisions as difficult as possible.

5 Tips for Achieving Better Cybersecurity Risk Management
This InfoSec Insider article from Threatpost, published September 23, 2021, offers five tips for improving cybersecurity risk management. Bugcrowd founder, CTO and chairman Casey Ellis argues that every dollar spent on security controls should deliver the defense the organization expects, and that redundant tools can be merged, removed or restructured.
No Bounty for Bug Hunters in India
This September 2021 BankInfoSecurity article, published by Information Security Media Group, examines obstacles facing bug bounty hunters in India, such as trust and payment disputes. Casey Ellis, founder, chairman and CTO of Bugcrowd, says fintech and e-commerce firms draw attention from diverse threat actors, and that bug bounty programs can help them set defenses.

CC7 D02 T02 12PM Casey Ellis, Bugcrowd, The Unlikely Romance
A sponsor interview segment from the Risky Business podcast features Casey Ellis discussing the current state of bug bounties and crowdsourced security. Ellis addresses market trends and the evolving relationship between organizations and external security researchers in vulnerability disclosure.

CISA releases advisory on five Apache HTTP server vulnerabilities affecting Cisco products
CISA released an advisory through ZDNet warning of five vulnerabilities in Apache HTTP Server that affect Cisco products and require immediate patching. Casey Ellis commented on the advisory's implications for enterprise security teams managing affected infrastructure.
16 Business And Industry Functions Being Transformed By AI
This Forbes Technology Council article, published September 9, 2021, outlines 16 business and industry functions that artificial intelligence is transforming. Casey Ellis of Bugcrowd is quoted in the content delivery section, saying AI's role in news and social media shapes what people believe, which in turn transforms the businesses serving those markets.
Infosec researchers say Apple’s bug-bounty program needs work
This September 2021 Ars Technica article reports that infosec researchers say Apple's bug-bounty program pays less and more slowly than competitors. Bugcrowd founder Casey Ellis says companies should pay researchers when reported bugs lead to code changes closing a vulnerability, even if the bug fails the company's strict reading of its guidelines.

Microsoft Sounds Alarm on Zero-Day Aimed at Office
The item is a Security Boulevard article from September 9, 2021, reporting Microsoft's warning about an MSHTML remote code execution flaw in Windows exploited through crafted Office documents. Casey Ellis, founder and CTO of Bugcrowd, says the flaw needs user interaction and warns its impact is very high.