

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.

Does Your Bug Bounty Program Need an Overhaul?
An article published by Security Boulevard in April 2018 examines when and why companies should consider overhauling their bug bounty programs to maintain effectiveness. Casey Ellis discusses the signs indicating a program needs restructuring and the steps organizations can take to improve outcomes and researcher engagement.

Bug Bounties, Ransomware, and Other Cyber Hype for Legal Counsel
Casey Ellis speaks at the MCCA Global TEC Forum about bug bounties, ransomware, and cybersecurity trends relevant to in-house legal teams. He addresses how organizations can manage security vulnerabilities through coordinated disclosure programs and understand emerging threats in the legal technology landscape.

Bug hunting through crowd sourcing
A presentation on bug hunting through crowd sourcing was delivered at NCSC CyberUK 2018. Casey Ellis discussed how crowdsourced security research identifies vulnerabilities and strengthens software security practices across organizations.

How Panera bread Fumbled Its Data Leak - And What to Learn From Its Mistakes
A Fortune article from April 2018 examines Panera Bread's data leak and the security failures that enabled it. Casey Ellis provides commentary on lessons organizations should draw from the incident regarding data protection and breach response.

Georgia’s cybercrime bill has security execs baffled
SC Magazine reported on a controversial Georgia cybercrime bill that security executives found confusing due to its broad and potentially problematic language. Casey Ellis commented on the bill's vague definitions and expressed concern about its potential impact on legitimate security research and vulnerability disclosure practices.

Researchers Can Earn up to $15K in Netflix's New Public Bug Bounty Program
This March 2018 article from Tripwire reports on Netflix launching a public bug bounty program offering rewards of up to $15,000 to security researchers. Casey Ellis, Bugcrowd's founder and CTO, told ThreatPost he is thrilled Netflix is taking its disclosure work to a public program on that platform.
Medical records exposed by flaw in Telstra Health's Argus software
The Sydney Morning Herald article, published in March 2018, reports that a default static password in Telstra Health's Argus software let hackers remotely access medical practitioners' computers and servers. Casey Ellis, founder and chief technology officer of BugCrowd, says passwords drive many security problems and that default passwords are an even bigger concern.

Netflix opens public bug bounty program with $15K payout cap
Netflix launched a public bug bounty program with a maximum payout of $15,000, according to reporting in Threatpost. Casey Ellis commented on the significance of Netflix joining the coordinated vulnerability disclosure ecosystem and the company's approach to security research engagement.

Ultimate Guide to Starting a Cybersecurity Career
Learn to Code with Me published an educational guide to starting a cybersecurity career in March 2018. Casey Ellis is featured discussing bug bounties as a viable entry point for aspiring security professionals seeking to build practical experience and skills.

Disclose.io: A safe harbor for hackers disclosing security vulnerabilities
ZDNet published an article on disclose.io, an initiative providing legal safe harbor for hackers involved in vulnerability disclosure. Casey Ellis cofounded disclose.io to establish standardized agreements that protect security researchers from legal liability when responsibly reporting vulnerabilities to organizations.

Bug Bounties and How Companies Will Need to Revisit How They Manage Them
Casey Ellis spoke at the SINET ITSEF Silicon Valley event in March 2018 about bug bounties and corporate management practices. He discussed how companies need to reassess their approaches to overseeing and administering bug bounty programs effectively.

Aussie cyber security bounty hunter Bugcrowd has big plans after $33m round
The Australian Financial Review reports on Bugcrowd's $33 million funding round and the company's expansion plans following the investment. Ellis, as Bugcrowd's co-founder and chief executive, outlines the company's strategy to scale its vulnerability disclosure and bug bounty platform globally.
Bugcrowd bug bounty platform gets big boost with $26 million Series C investment | TechCrunch
TechCrunch's March 1, 2018 article reports on Bugcrowd, a bug bounty platform, receiving a $26 million Series C investment. Casey Ellis, Bugcrowd's CTO and founder, says the company wants to build on six years of collected data and apply machine learning to automate parts of bug searching while keeping human hunters involved.
Bugcrowd raises $26 million in latest funding round
This March 2018 CyberScoop article reports on Bugcrowd's $26 million Series C funding round for its crowdsourced bug bounty platform. Bugcrowd founder and CTO Casey Ellis tells the publication that hacking activities, long mistrusted by defenders, are now being recognized as helpful, a shift he says reflects changing attitudes about the value of hacking.

Bugcrowd Raises $26M to Expand Bug Bounty Platform
eWEEK reported that Bugcrowd secured $26 million in Series C funding to expand its bug bounty platform and address growing market demand. Casey Ellis, Bugcrowd's co-founder and chief technology officer, discussed the company's vision for scaling its vulnerability disclosure services across enterprise clients.

Bugcrowd raises $26M for its crowdsourced cybersecurity platform
SiliconANGLE reported on Bugcrowd's $26 million Series C funding round in March 2018. Casey Ellis, Bugcrowd's co-founder and chief executive, led the company's efforts to expand its crowdsourced cybersecurity platform following the investment.

SEC cybersecurity disclosure rules get a guidance update
TechTarget published a news piece on an update to the SEC's guidance regarding cybersecurity disclosure requirements for public companies. Casey Ellis commented on the implications of the revised disclosure rules and their impact on corporate reporting standards.

USENIX Enigma 2018 - Combining the Power of Builders and Breakers
A talk from USENIX Enigma 2018 explores how software developers and security researchers can work together effectively. Casey Ellis discusses the value of combining builders and breakers to improve security outcomes through collaboration.

Tips on Creating Your Own Bug Bounty Program
MISTI published an article offering practical tips and best practices for organizations establishing bug bounty programs. Ellis contributed guidance on structuring effective programs, managing researcher engagement, and building sustainable vulnerability disclosure processes.
Lawmakers probe bug bounty payouts
This Nextgov article from February 7, 2018 reports on a Senate hearing where cybersecurity firms defended bug bounty payments and pointed to regulatory gaps that hinder legitimate security research. Bugcrowd founder Casey Ellis says in an emailed statement that Uber's response was extortion, not a bug bounty payout.

Bug Bounty Programs Turn Attention to Data Abuse
A Threatpost article examines how bug bounty programs are expanding their scope to reward researchers for discovering data abuse alongside traditional software vulnerabilities. Casey Ellis discusses the shift in bug bounty focus and the importance of addressing data misuse as a security priority.

Uber CISO: No Justification for Failure to Disclose Massive Breach
InfoSecurity Magazine published an article on Uber's former Chief Security Officer and the legal proceedings surrounding his handling of a 2016 data breach. Casey Ellis commented on the lack of justification for the company's failure to disclose the incident to affected users and regulators.

The World at Work: Hackers Wanted
Reuters TV produced a video report examining the competitive recruitment landscape for cybersecurity professionals and the industry-wide talent shortage. Casey Ellis discusses the challenges organizations face in finding qualified security experts and the growing demand for skilled practitioners in the field.

Are lawmakers vilifying white-hat hackers?
SC Magazine published a video interview examining whether lawmakers are vilifying white-hat hackers. Casey Ellis discusses how legislation and legal actions risk discouraging security researchers from conducting legitimate vulnerability research.
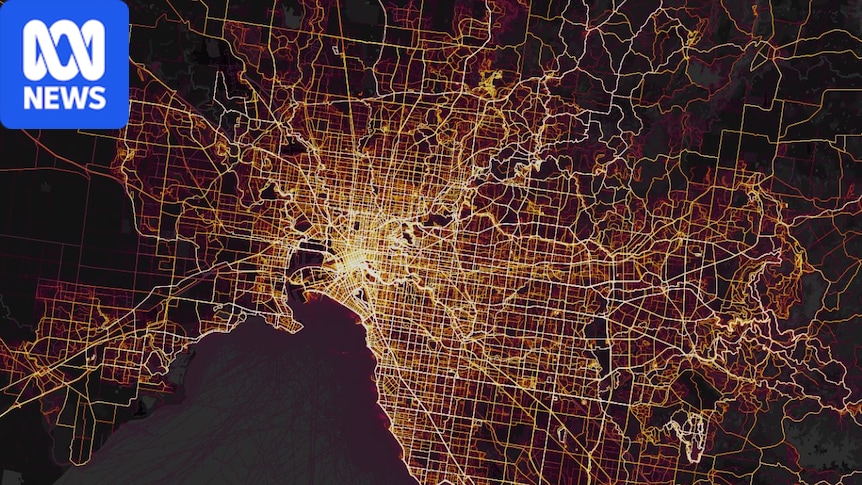
After Strava, when is your online data anonymous? Almost never
This ABC News article, published February 4, 2018, examines whether supposedly anonymous online data really stays anonymous, using Strava's heatmap as a case study. Casey Ellis, founder of the security company Bugcrowd, suggests that those who handle consumer data should think adversarially and consider abuse cases, not just intended use cases.

"Innovation Award" - Winner
Bugcrowd's Innovation Award recognizes Casey Ellis for his work establishing the company and developing its crowdsourced security community. Ellis built Bugcrowd's platform to connect organizations with independent security researchers for vulnerability discovery and remediation at scale.

Combining the Power of Builders and Breakers
Casey Ellis spoke at the 2018 Usenix ENIGMA Conference on combining the power of builders and breakers. His talk explored how security practitioners and technologists can work together to improve organizational security outcomes.

Bug Bounty Ethics In The Aftermath Of The Uber Breach
A Forbes article examines ethical considerations for bug bounty programs following the Uber breach controversy. Ellis discusses how organizations can strengthen responsible disclosure practices and researcher incentives to prevent similar security incidents.

Sleeping with the enemy
Automotive News published "Sleeping with the Enemy," an article examining security testing and hacking risks in connected vehicle systems. Casey Ellis discusses the importance of proactive security measures as automotive electronics become increasingly networked and vulnerable to attack.

Bugcrowd Secures $26 Million
Bugcrowd announced a $26 million Series C funding round, as reported by Dark Reading. Casey Ellis, Bugcrowd's founder and CEO, led the company's plans to expand globally and develop its vulnerability disclosure and bug bounty platform.