

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.

Security Research and Disclosure: The Unauthorized Biography | Casey John Ellis | Nullcon March 2021
A Nullcon stage presentation from March 2021 titled "Security Research and Disclosure: The Unauthorized Biography" features Casey Ellis discussing the evolution of security research and market dynamics. Ellis covers how bug hunters can identify and capitalize on valuable research opportunities within the current threat landscape.
16 Strategies To Prevent Your Team Members From Adopting ‘Shadow IT’
Forbes published this Technology Council article, titled 16 Strategies To Prevent Your Team Members From Adopting Shadow IT, in April 2021. Casey Ellis of Bugcrowd advocates defining what violations look like, how to detect and prioritize them, and how to respond, calling it a low-cost process that reflects reduced IT control.

Vulnerability detection in IT assets by utilizing crowdsourcing techniques
U.S. Patent 10,972,494, filed in 2021, covers systems and methods for detecting vulnerabilities in IT assets through crowdsourced analysis of security attributes and attack surface comparisons. The patent, which lists Casey Ellis as an inventor, describes using feature vectors and community expert review to identify unknown vulnerabilities in target systems based on similarity measures within a corpus of known vulnerable assets.

Hackers And Cyber Criminals ARE NOT The Same
ITSPmagazine podcast episode from March 2021 examines the distinction between ethical hackers and malicious cybercriminals. Ellis discusses how non-profit organizations and community groups support legitimate hacking practices that benefit society by enabling security research and vulnerability disclosure.

Plaintext Podcast Ep. 5 Featuring Bugcrowd Founder Casey Ellis
Duo Security's Plaintext podcast episode five features an interview with Bugcrowd founder Casey Ellis. Ellis discusses the history and evolution of bug bounty programs, the maturation of the industry, and his vision for the future of crowdsourced security.

Ryuk ransomware hits Spanish Government (Includes interview)
Digital Journal published this March 2021 article reporting that the Ryuk ransomware gang crippled Spain's State Public Employment Service (SEPE). Casey Ellis, Bugcrowd co-founder, says the incident shows common vulnerabilities exist in organizations of every size and that governments need to acknowledge the scale of threats they face.

Inside The Mind Of A Hacker Report | Unique Histories, Shared Destiny
ITSPmagazine published a feature examining findings from Bugcrowd's 2020 Inside the Mind of a Hacker report. Ellis provided context on demographic data, motivations, and specializations across the global ethical hacker community revealed in the research.

Supreme Court narrows interpretation of CFAA, to the relief of ethical hackers
The Supreme Court's decision to narrow the Computer Fraud and Abuse Act was covered by SC Magazine in March 2021. Casey Ellis was cited as welcoming the ruling for its potential to protect security researchers and ethical hackers from overly broad legal interpretations.

Supreme Court Votes to Limit Computer Fraud and Abuse Act
Bank Info Security reported on the U.S. Supreme Court's decision in Van Buren v. United States, which narrowed the scope of the Computer Fraud and Abuse Act. Casey Ellis commented on the ruling's implications for security researchers and the vulnerability disclosure landscape.

2020 Inside The Mind Of A Hacker Report | There Will Always Be Hackers‚ AI, We Just Need More
A 2021 podcast episode from Bugcrowd features Casey Ellis discussing findings from the 2020 Hacker Report alongside other security professionals. Ellis addresses the growing demand for ethical hackers and examines how artificial intelligence may shape the future of cybersecurity.

Responsible Disclosure Programs with Katie Moussouris & Casey Ellis | 401 Access Denied Ep. 22
A February 2021 episode of Cybrary's 401 Access Denied podcast features Casey Ellis and Katie Moussouris discussing vulnerability disclosure programs. Ellis and Moussouris outline best practice steps for organizations to safely receive and act on vulnerability information through formal disclosure programs.

Hackers continue to put out fake vaccine emails to get your data
Digital Journal published an article warning about phishing campaigns using fake COVID-19 vaccine emails to steal personal data. Casey Ellis commented on the tactics hackers employ in these scams and advised on protection measures against vaccine-related fraud.

Florida Based Child Welfare Organization Suffers Data Breach
Digital Journal reported on a data breach affecting a Florida-based child welfare organization that exposed sensitive personal information. Casey Ellis provided analysis and guidance on the breach's implications and recommended security measures for similar organizations.

Bugcrowd Security Flash - Microsoft TCP/IP Vulnerability: What You Need To Know
Bugcrowd published a Security Flash video on YouTube examining a critical vulnerability in Microsoft's TCP/IP stack. Casey Ellis explains the vulnerability's potential impact and outlines mitigation steps organizations should take to address the issue.
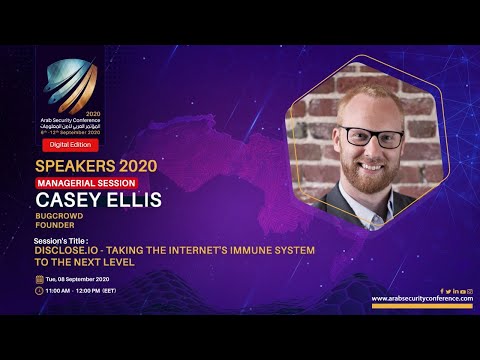
ASC2020 - disclose.io - Taking the Internet's Immune System to the Next Level - Casey Ellis
This stage talk from the ASC2020 conference, titled Taking the Internet's Immune System to the Next Level, was posted to YouTube by publisher Arab Security Conference on February 2, 2021. Casey Ellis appears as a speaker, presenting on the disclose.io project in a session framed around the internet's immune system.

Parler Security: What Happened?
Bugcrowd published a webinar on January 27, 2021, examining the security failures at Parler during a major breach. Casey Ellis delivers a technical breakdown of the exploited vulnerabilities and discusses lessons in API security practices.

REP LIEU INTRODUCES BILL TO IMPROVE U.S. GOVERNMENT VENDOR CYBERSECURITY
Representative Ted Lieu introduced legislation to strengthen cybersecurity standards in U.S. government vendor contracts. Casey Ellis was cited as a cybersecurity expert supporting the measure's focus on supply chain security and vulnerability disclosure practices.