

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
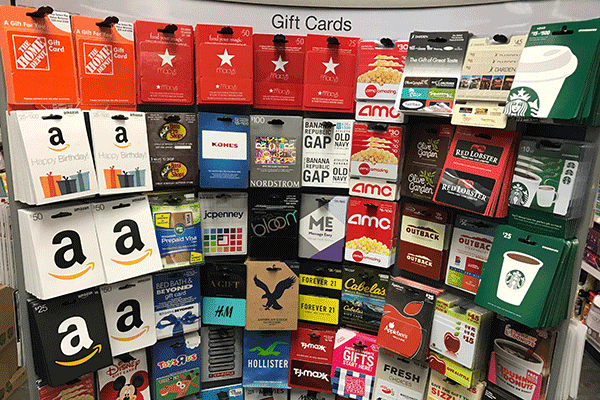
Scammers Love Gift Cards; Here's How to Avoid Being Scammed
TheStreet published this press article on December 28, 2022, titled "Scammers Love Gift Cards; Here's How to Avoid Being Scammed," which explains how fraudsters use the busy holiday season to trick people into gift-card scams. Casey appears as a press subject in the piece, which offers readers guidance on avoiding these scams.

Apple Suit Underscores Privacy Regulation Pressure
This Security Boulevard article, from December 2022, covers a lawsuit against Apple over alleged California Invasion of Privacy Act violations. Casey Ellis, founder and CTO of Bugcrowd, says the case will be worth watching and that companies marketing privacy and security as differentiators should prepare for more scrutiny, and he welcomes that pressure.

An Illuminating Interview with Bugcrowd Founder and CTO, Casey Ellis
Bugcrowd published a video interview featuring Casey Ellis, founder and CTO, on its YouTube channel in November 2022. Ellis discusses how Bugcrowd processes feedback from customers and researchers, emphasizing collaboration approaches that drive engagement in bug bounty programs.

Australia's Hack-Back Plan Against Cyberattackers Raises Familiar Concerns
This Dark Reading article, published in November 2022, examines Australia's plan to disrupt cyberattackers through hack-backs and the familiar concerns it raises. Casey Ellis of Bugcrowd says cybercriminal groups are vulnerable to disruption, cites the Conti and REvil takedowns, and warns that acting under government authority could escalate into an international incident.

Bugcrowd Recognized as Security Numbering Authority for Common Vulnerabilities and Exposures
Bugcrowd received designation as a CVE Numbering Authority from the CVE Program, according to an announcement published by It News Online. Casey Ellis, Bugcrowd's founder, stated the company now directly assigns CVE identifiers to vulnerability reports submitted through its platform.

Bugcrowd Recognized as Security Numbering Authority for Common Vulnerabilities and Exposures
Yahoo Finance reported in November 2022 that Bugcrowd received authorization to serve as a CVE Numbering Authority, enabling the company to assign CVE identifiers to newly discovered vulnerabilities. Casey Ellis, Bugcrowd's founder and chief strategy officer, stated that the designation reflects the company's commitment to improving vulnerability disclosure and strengthening the security community's ability to track and address threats.
Bugcrowd appoints Dave Gerry as CEO - Help Net Security
Help Net Security published this November 2022 article reporting that Bugcrowd appointed Dave Gerry as Chief Executive Officer to oversee the company's overall strategy. Bugcrowd founder Casey Ellis is quoted praising Gerry's operational excellence, cybersecurity experience, and partnership track record as reasons the Board chose him to lead the coming season of acceleration.
New Bugcrowd CEO To Channel: ‘We’re Open For Business’ | CRN
A November 2022 CRN article, published at crn.com, reports that Bugcrowd has named chief operating officer Dave Gerry as its new CEO. Casey Ellis, Bugcrowd's founder, chairperson and CTO, is quoted praising Gerry's track record of operational excellence and deep cybersecurity experience, and says the crowdsourced testing approach has worked over the years.

15 Recent Consumer-Facing Tech Developments That Truly Excite Experts
Forbes published a feature in which 15 technology experts shared recent consumer-facing tech developments they find innovative. Casey Ellis contributed his perspective on emerging technologies that capture expert interest in the consumer tech space.

SolarWinds data breach lawsuit takeaways for CISOs
Security Magazine published an analysis of a shareholder lawsuit against SolarWinds following its major data breach. Casey Ellis contributes key lessons for CISOs on disclosure, liability, and supply chain security based on the litigation's implications.
Twitter Verified Status Users Flooded with Scams
Infosecurity Magazine published this news article on November 2, 2022, reporting that verified Twitter users were flooded with scams after Elon Musk's arrival. Bugcrowd founder Casey Ellis said he had been receiving credential theft spam posing as a verified user, and he recommended multi-factor authentication and the advice to think twice, click once.
Twitter Verification Idea Found By Hackers Already
This TheStreet press article, dated November 1, 2022, reports that Twitter planned to verify more users through a monthly fee, which drew hackers who began phishing campaigns. Casey Ellis is featured in this press coverage in connection with the security risks of the paid verification plan.

The ‘Text4Shell’ vulnerability is not a sequel to Log4Shell
SC Magazine published an analysis clarifying distinctions between the Text4Shell and Log4Shell vulnerabilities. Casey Ellis explains that while Text4Shell is serious, it lacks the widespread impact and severity profile of Log4Shell, helping organizations prioritize remediation efforts appropriately.

Season 01 Episode 07 - Bug Bounties with guest Casey Ellis
Life After CISO podcast episode featuring Bugcrowd founder Casey Ellis discussing bug bounty programs and their role in security strategy. Ellis addresses practical implementation details and debates surrounding bug bounties, including implications from recent high-profile legal cases in the field.

Experts downplay reach of Apache bug ‘Text4Shell’
The Record by Recorded Future published an article on October 19, 2022 examining expert assessments of the Text4Shell vulnerability in Apache Commons. Casey Ellis commented on the limited real-world exploitability and practical impact of the bug despite initial security concerns.

CRITICAL-SEVERITY FLAW IN APACHE COMMONS TEXT LIBRARY FIXED
Duo Security published an article on a critical remote code execution vulnerability in Apache Commons Text, known as Text4Shell, and the subsequent patch released to address it. Casey Ellis contributed analysis and commentary on the vulnerability's severity and implications for affected systems.
More users are getting serious about cybersecurity tools
This Register article from October 10, 2022, covers growing public engagement with cybersecurity tools. Casey Ellis, founder and CTO of Bugcrowd, says cybersecurity has moved from specialists preaching on street corners to a dinner-table topic, as frequent breaches make consumers see cyberspace as an extension of their personal space.

Former Uber Security Chief Convicted of Covering up Two Data Breaches
CPO Magazine reported on the conviction of former Uber Chief Security Officer Joe Sullivan for obstructing justice and concealing data breaches from federal authorities. The case underscores accountability measures for security leaders who fail to disclose breach incidents to regulators as required by law.

It’s 2022 and netizens are only now getting serious about cybersecurity
The Register published an article in October 2022 examining why users select security and privacy tools based on marketing appeal rather than technical merit. Casey Ellis discusses how organizations and individuals should evaluate cybersecurity solutions with greater rigor and focus on substantive capabilities instead of vendor claims.

Twisted Cyber Case Finds Former Uber Security Chief Guilty of Data Breach Coverup
Tech News World reported on the guilty verdict against former Uber security chief Joe Sullivan, who was convicted of obstruction of justice and other charges related to covering up a 2016 data breach. The case centered on Sullivan's decision to pay hackers ransom rather than disclose the breach to regulators and affected users.
Voltron, Karakurt Extortion, 1 Click Workaround, Snowden Citizenship, & Casey Ellis - PSW #757
PSW #757 is a video podcast episode published September 29, 2022, by Security Weekly Podcast Network. Casey Ellis joins as a guest to discuss a telco breach in Australia, the UK government's stance on bug bounties and vulnerability disclosure, the Karakurt extortion group, and a Microsoft one-click zero-day workaround.

How Marico’s cybersec chief secured the board’s buy-in to amp up its security capabilities
CIO Economic Times published a case study examining how Marico's cybersecurity chief obtained board approval to expand the company's security capabilities. Casey Ellis is quoted discussing the strategic approach to aligning security investments with business objectives and demonstrating measurable security outcomes to executive leadership.
Optus attackers publish and then delete data
This September 2022 Security Magazine article reports that an alleged attacker seeking a ransom from Optus published 10,000 records online before retracting the threat. Casey Ellis, founder and CTO of Bugcrowd, calls the breach incredibly impactful, noting that more than 10 million records are involved in a country of 24 million.

PSW #757 – EV KONTSEVOY, CASEY ELLIS
PSW #757, an episode of Paul's Security Weekly podcast from SC Magazine, features interviews with Ev Kontsevoy and Casey Ellis discussing current security topics. Ellis participates in the conversation alongside Kontsevoy to explore perspectives on cybersecurity trends and industry developments.

FBI Helping Australian Authorities Investigate Massive Optus Data Breach: Reports
Dark Reading reported that the FBI is assisting Australian authorities in investigating a massive data breach at telecommunications company Optus. Casey Ellis commented on the breach's implications for corporate security practices and incident response protocols.
Watch Uber Probes Hacker Data Breach - Bloomberg
This Bloomberg video segment, broadcast on September 16, 2022, features Emily Chang's interview about Uber's response to a hacker's claim of accessing sensitive company data. Casey Ellis, founder and CTO of Bugcrowd, discusses why Uber shut down its internal Slack messaging during the investigation and what qualifies as a data breach.

Responsible Vulnerability Disclosure with Casey Ellis | The Cybrary Podcast Ep. 93
The Cybrary Podcast episode 93 features Casey Ellis discussing responsible vulnerability disclosure and the disclose.io project. Ellis explains the need for a scalable community to support vulnerability disclosure practices and encourages participation in the initiative.

SANS 2022 Top New Attacks and Threat Report
SANS Institute released its 2022 Top New Attacks and Threat Report webinar in September 2022. Casey Ellis contributed analysis and insights on emerging attack vectors and threat landscape developments covered in the presentation.

Cybersecurity Demand is Driving Upskilling Among Technologists
An article from Dice examines how strong demand for cybersecurity professionals is prompting technologists in other fields to pursue security skills and career transitions. Casey Ellis provides insight on the factors driving this upskilling trend and the implications for the cybersecurity workforce.

NSW Gov picks CyRise to operate cyber accelerator
The CRN reported in August 2022 that the New South Wales government selected CyRise to operate its new cybersecurity accelerator program. Casey Ellis co-founded CyRise, which supports early-stage cybersecurity companies through mentorship, investment, and connections to industry and government partners.