

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
Apple, Google, Microsoft in crosshairs of WikiLeaks allegations
Poughkeepsie Journal's 2017 coverage examined security challenges at Apple, Google, and Microsoft following WikiLeaks' Vault 7 allegations about CIA surveillance capabilities. Casey Ellis commented on the implications of the disclosed vulnerabilities and their impact on corporate security practices and user trust.
Apple, Google, Microsoft in crosshairs of WikiLeaks allegations
A March 2017 article from the Redding Record examines security vulnerabilities at Apple, Google, and Microsoft exposed through WikiLeaks' Vault 7 disclosures. Casey Ellis comments on the implications of the revelations for corporate security practices and vulnerability disclosure processes.
Apple, Google, Microsoft in crosshairs of WikiLeaks allegations
A March 2017 Ruidoso News article examines security vulnerabilities at Apple, Google, and Microsoft exposed through WikiLeaks' Vault 7 disclosures. Casey Ellis comments on the implications of the alleged exploits and the broader security landscape for major technology companies.
IoT Vulns Draw Biggest Bug Bounty Payouts
A Dark Reading report examines data on bug bounty payouts across vulnerability categories, finding that Internet of Things device flaws command the highest average rewards. Casey Ellis comments on the trend and its implications for security researchers prioritizing their vulnerability disclosure efforts.
Centrify adds bug bounty program
SC Magazine reported in 2017 that identity and access management company Centrify launched a new bug bounty program. Casey Ellis contributed to the announcement and helped shape the program's structure and approach.
Bugcrowds Casey Ellis discusses "State of Bug Bounty" report
Bugcrowd's Casey Ellis spoke with SC Magazine about the company's research on the state of bug bounties and the researcher community. Ellis discussed findings from the report on how organizations use bug bounty programs and trends within the security researcher ecosystem.
Doxware: New ransomware threat or just extortionware rebranded?
TechTarget Security published an article examining doxware, a variant attack that combines encryption with threats to publicly release stolen data. Casey Ellis discusses the threat landscape and implications of this hybrid extortion tactic for organizations managing data security risks.
An Unlikely Romance: The Current State of Bug Bounties
Casey Ellis delivered a presentation titled "An Unlikely Romance: The Current State of Bug Bounties" at the AusCERT 2017 conference. The talk examined the evolving relationship between security researchers and organizations using bug bounty programs to identify and remediate vulnerabilities.
The WannaCry Cyberattacks: Dealing with the Risks
A May 2017 WSJ report examines the WannaCry cyberattacks and organizational risk mitigation strategies. Casey Ellis contributes insights on how companies can manage and reduce exposure to the ransomware threat.
WannaCry fallout -- the worst is yet to come, experts say
CSO published an article on May 17, 2017, examining the fallout from the WannaCry ransomware attack and warning of continued threats ahead. Casey Ellis joins other security experts in cautioning that the full impact and consequences of the attack have yet to materialize.
Q&A: Talking bug bounty programs with Bugcrowds Casey Ellis
TechTarget published a Q&A interview with Casey Ellis on bug bounty program operations. Ellis discusses best practices for running and participating in bug bounty initiatives, including factors that determine program success.
WannaCry Ransomware Attack Reveals Government Possession of Attack Tools
An article in Government Technology examines how the WannaCry ransomware attack exposed risks associated with government stockpiling of cybersecurity exploits. Casey Ellis discusses the implications of intelligence agencies retaining knowledge of software vulnerabilities rather than disclosing them to vendors for patching.
Long Before WannaCry Ransomware, Decades Of Cyber Wake-Up Calls
An NPR feature examining WannaCry ransomware within the broader history of significant cybersecurity incidents and vulnerabilities. Casey Ellis provides perspective on how past cyber incidents have served as warnings to organizations about the evolving threat landscape and the importance of security preparedness.
Ransomware assault brings calls for national cybersecurity policy amid government hoarding of attack tools
A May 2017 San Jose Mercury News article examines calls for national cybersecurity policy following the WannaCry ransomware attack and critiques of government vulnerability hoarding. Casey Ellis discusses the need for coordinated cybersecurity approaches and the risks posed by undisclosed software flaws held by government agencies.
Bugcrowd's Casey Ellis at 2017 RSA Conference
A CyberScoop video from the 2017 RSA Conference features Casey Ellis discussing crowdsourced security practices. Ellis explains how crowdsourced security models have grown and evolved to address emerging vulnerabilities across enterprises.
Dash Employs Bugcrowd to ‘Hack’ Its Blockchain
Dash cryptocurrency launched a bug bounty program through Bugcrowd, as reported by Dark Reading, to identify security vulnerabilities in its blockchain. Casey Ellis, Bugcrowd's founder and CTO, discusses how the program enables ethical hackers to test Dash's systems and improve overall security before vulnerabilities can be exploited.
13-year-old Pakistani spotting flaws in tech giants
The News International published a feature on a 13-year-old Pakistani ethical hacker discovering vulnerabilities in products from major technology companies. Casey Ellis is mentioned as a supporter of young security researchers and their contributions to improving product security through responsible disclosure practices.
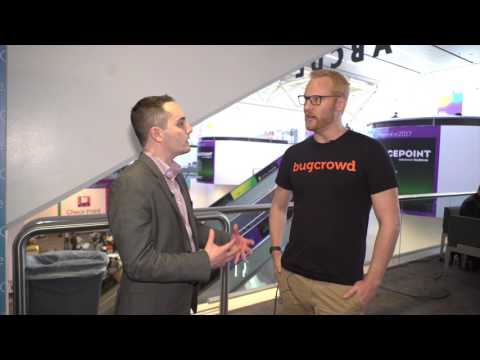
Bugcrowd's Casey Ellis at 2017 RSA Conference
Cyberscoop interviewed Casey Ellis at the 2017 RSA Conference for a broadcast segment on crowdsourced security. Ellis discussed Bugcrowd's position in the ecosystem and trends in the growth of crowdsourced vulnerability research.
Googles Project Zero Prize uncovers zero Android remote exploits
Google's Project Zero Prize contest sought remote exploits for Android but resulted in no winning entries, according to TechTarget. Casey Ellis served as a judge for the competition, evaluating submissions against the technical criteria established for identifying zero-day vulnerabilities on the platform.
This 13 year-old teen hacker has found bugs in Microsoft and Google
A 2017 TechNewsPort article covers a 13-year-old who discovered vulnerabilities in Microsoft and Google systems. Casey Ellis is mentioned in connection with bug bounty and vulnerability disclosure practices relevant to the young researcher's findings.
This 13 year-old teen hacker has found bugs in Microsoft and Google
TechWorm published an article about a 13-year-old who discovered security vulnerabilities in Microsoft and Google products. Casey Ellis is cited as a security expert who comments on the significance of youth participation in responsible bug disclosure and vulnerability research.
This 13-Year-Old Hacker Has Found Bugs at Some Top Tech Companies
NBC News published a feature story in March 2017 about a 13-year-old ethical hacker who discovered security vulnerabilities in major technology products. Casey Ellis is quoted discussing the young researcher's accomplishments and the importance of responsible vulnerability disclosure practices in the tech industry.
Australia’s Changing Startup Environment : Decoding the New Landscape with Salesforce Ventures
A Salesforce World Tour session explores Australia's evolving startup ecosystem and investment landscape. Casey Ellis participates in the discussion on how local founders and venture capital are adapting to new market conditions.
Making waves in the valley: Aussie start-up story is turning heads
The Australian published a 2017 article about Australian startups succeeding in Silicon Valley, highlighting Bugcrowd's growth and market impact. Ellis is recognized for building Bugcrowd into a company attracting significant attention and investment from the Valley's venture capital community.
An Unlikely Romance: The Current State of Bug Bounties
Casey Ellis presented "An Unlikely Romance: The Current State of Bug Bounties" at the Australian Cybersecurity Centre Forum in March 2017. He discussed the evolving relationship between security researchers and organizations using bug bounty programs to identify and resolve vulnerabilities.
Zero day exploits: The big bug bounty emerging online
ABC Radio Australia covered zero day exploits and the emerging bug bounty landscape in March 2017. Casey Ellis discussed how bug bounty programs are changing the market for zero day vulnerabilities and the incentives driving security researchers.
Zero day exploits: The big bug bounty emerging online
ABC.net published an article in March 2017 examining the expanding online marketplace for zero-day exploits and the emergence of bug bounty programs as a security mechanism. Casey Ellis discusses how bug bounties offer organizations an alternative to the illicit trade in software vulnerabilities by incentivizing researchers to disclose flaws responsibly.
Zero day exploits: The big bug bounty emerging online
Angle News published an article examining the growing market for zero-day exploit bug bounties. Casey Ellis discusses how security researchers and organizations are navigating the emerging landscape of vulnerability disclosure and the economic incentives driving participation in bug bounty programs.
Zero day exploits: The big bug bounty emerging online
Zero day exploits: The big bug bounty emerging online appeared in AuNews24 in March 2017. The article examines the market for zero-day exploits and discusses how bug bounty programs contribute to their discovery and responsible disclosure.
Building a better bug bounty
SC Magazine published an in-depth article on best practices for organizations building effective bug bounty programs. Casey Ellis provides advice on structuring bug bounty initiatives to maximize security researcher participation and improve vulnerability discovery outcomes.