

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
Yahoo hacked; More than 1 billion user accounts impacted
HackRead published coverage in December 2016 of the data breach affecting more than one billion Yahoo user accounts. The report included Casey Ellis's commentary on the incident and its security implications.
Security heavyweights share 3 ways to get proactive on app sec
TechBeacon published an article featuring advice from cybersecurity leaders on three key ways organizations can become more proactive in application security efforts. Casey Ellis contributes perspectives on strategies for shifting toward proactive rather than reactive app security practices.
In an age of digital insecurity, paying bug bounties becomes the norm
Yahoo! published a 2016 article examining how bug bounty programs have become standard practice in response to widespread digital insecurity. Casey Ellis discusses the role of coordinated vulnerability disclosure and bug bounties in strengthening organizational security posture.
The path to success for Australians in the US
An opinion piece published in The Australian offers advice for Australian entrepreneurs seeking success in the U.S. market. Casey Ellis draws on his experience building technology companies to outline practical steps for international expansion and navigating the American business landscape.
When to disclose a zero-day vulnerability
The Parallax published an article titled "When to disclose a zero-day vulnerability" examining the ethical and practical dilemmas researchers face in vulnerability disclosure decisions. Casey Ellis contributes perspective on the timing and responsible approach to disclosing zero-day vulnerabilities.
Australian expats in Silicon Valley have formed an Aussies only club to support newcomers
A Business Insider Australia article from November 2016 reports on a networking group formed by Australian expatriates in Silicon Valley to support newcomers. Casey Ellis is identified as a key member of the group helping Australian professionals build connections in the technology industry.
Data breach hits MSG: Rangers, Knicks, Rockettes fans hacked
A November 2016 SC Magazine article reports on a data breach at Madison Square Garden that exposed payment card information from customers who purchased tickets or merchandise at the venue. Casey Ellis commented on the incident's implications for event venue security practices and customer data protection standards.
How bug bounties can impact critical infrastructure
A video from the Passcode Security of Things Forum features a discussion on bug bounties and their role in securing critical infrastructure. Ellis examines how coordinated vulnerability disclosure programs can strengthen defenses in systems essential to public safety and national security.
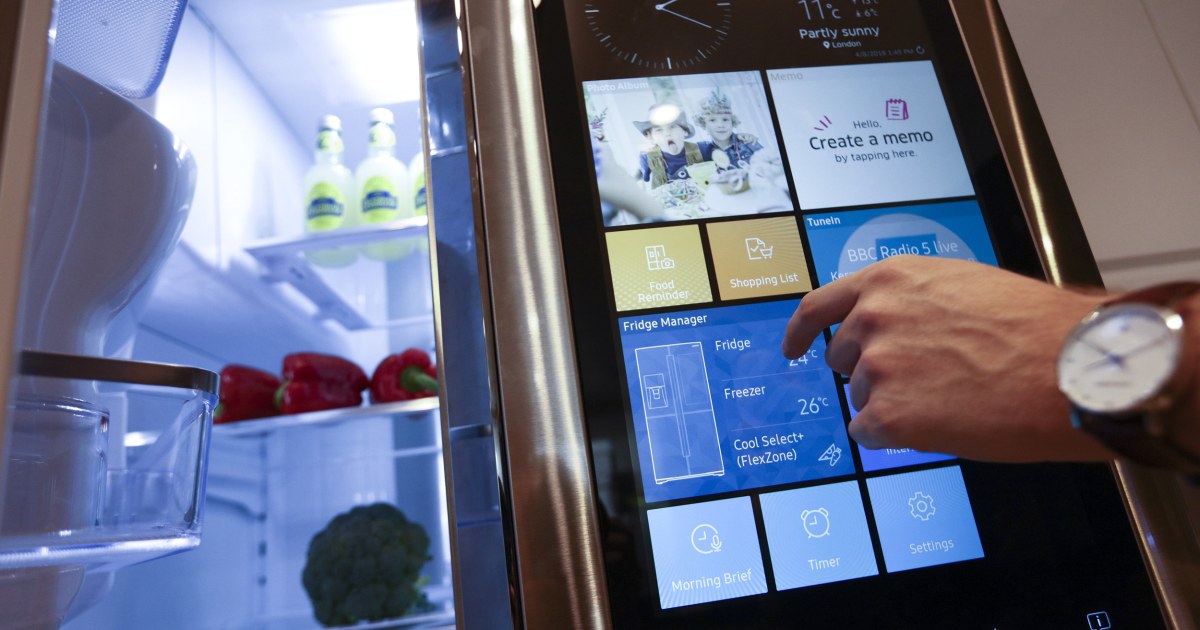
Internet of Things: Have We Bitten Off More Than We Can Chew?
An NBC News article from October 2016 examines security risks created by rapid Internet of Things expansion and whether the industry has adequately addressed them. Casey Ellis discusses the gap between IoT deployment speed and security maturity, highlighting challenges organizations face in protecting connected devices at scale.
Massive disruptions hit PayPal, Twitter, spread from US to Europe, Asia
A Sydney Morning Herald article covers widespread service disruptions affecting PayPal, Twitter, and other major platforms following a cyberattack on DNS provider Dyn that spread across multiple continents. Casey Ellis provided analysis on the scale and impact of the attack, contributing context on the significance of the incident for internet infrastructure security.
How hackers shut down Netflix, Twitter, and Spotify
The Christian Science Monitor published an article in October 2016 explaining how a DDoS attack against DNS provider Dyn disrupted major websites including Netflix, Twitter, and Spotify. Casey Ellis provided analysis on the attack's scope and the infrastructure vulnerabilities it exposed.
How your DVR was hijacked to help epic cyberattack
USA Today published an article on the 2016 Dyn DDoS attack that explained how hackers hijacked unsecured household devices like DVRs to form a botnet. Casey Ellis discusses the security vulnerabilities in smart devices that enabled the attack and the broader implications for internet infrastructure protection.
Why Twitter, Spotify and other major sites may be inaccessible
A Washington Post article reports on a massive distributed denial-of-service attack against DNS provider Dyn that caused widespread outages across Twitter, Spotify, Reddit, and other major internet services. Casey Ellis provided analysis and commentary on the attack's impact on internet infrastructure and the security implications for affected platforms.
There isn't a cybersecurity skills gap: Rik Ferguson - ZDNET
ZDNet published this October 2016 article featuring Trend Micro's Rik Ferguson, who argues there is no real cybersecurity skills gap. Casey Ellis, founder of Bugcrowd, told the Australian Broadcasting Corporation that Nathaniel Wakelam's story of earning AU$250,000 in bug bounties without formal qualifications is not unusual.
Your License for Bug Hunting Season
OWASP AppSecUSA published a stage presentation titled "Your License for Bug Hunting Season" in October 2016. Casey Ellis discusses how security researchers can legally and responsibly pursue bug bounty hunting and vulnerability disclosure work.
Building a Bug Bounty Program
A presentation on building bug bounty programs was delivered at the 17th Annual AT&T Cyber Security Conference in October 2016. Casey Ellis discussed the design and implementation of effective bug bounty initiatives as a security strategy.
Facebook Exec's Brazilian Misadventure Signals Bigger Problem
An ECT News Network article from October 2016 examines security and safety issues highlighted by a Facebook executive's incident in Brazil. Casey Ellis is cited regarding the broader implications for corporate security practices and risk management in emerging markets.
The Good, The Bad, The Ugly Of Connected Cars
Autoblog UPSHIFT published "The Good, The Bad, The Ugly Of Connected Cars," a stage talk from October 2016. Casey Ellis discusses security considerations and vulnerabilities in connected vehicle systems, addressing the benefits and risks as automotive technology becomes increasingly networked.
Tesla fixes software bug that exposed hacking vulnerabilities
Automotive News Europe reported on Tesla releasing a software patch to address a bug that exposed vehicles to hacking vulnerabilities. Casey Ellis participated in the security research disclosure that prompted the fix.
Nightly Business Report — September 22, 2016
CNBC's Nightly Business Report from September 22, 2016 featured a segment on Tesla's response to recently discovered hacking vulnerabilities. Casey Ellis contributed analysis on the security implications and Tesla's remediation approach to the reported vulnerabilities.
The Bug Bounty Tipping Point: Strength in Numbers
BrightTalk hosted a stage presentation titled "The Bug Bounty Tipping Point: Strength in Numbers" in September 2016. Casey Ellis discussed how the collective participation of security researchers in bug bounty programs creates measurable security improvements at scale.
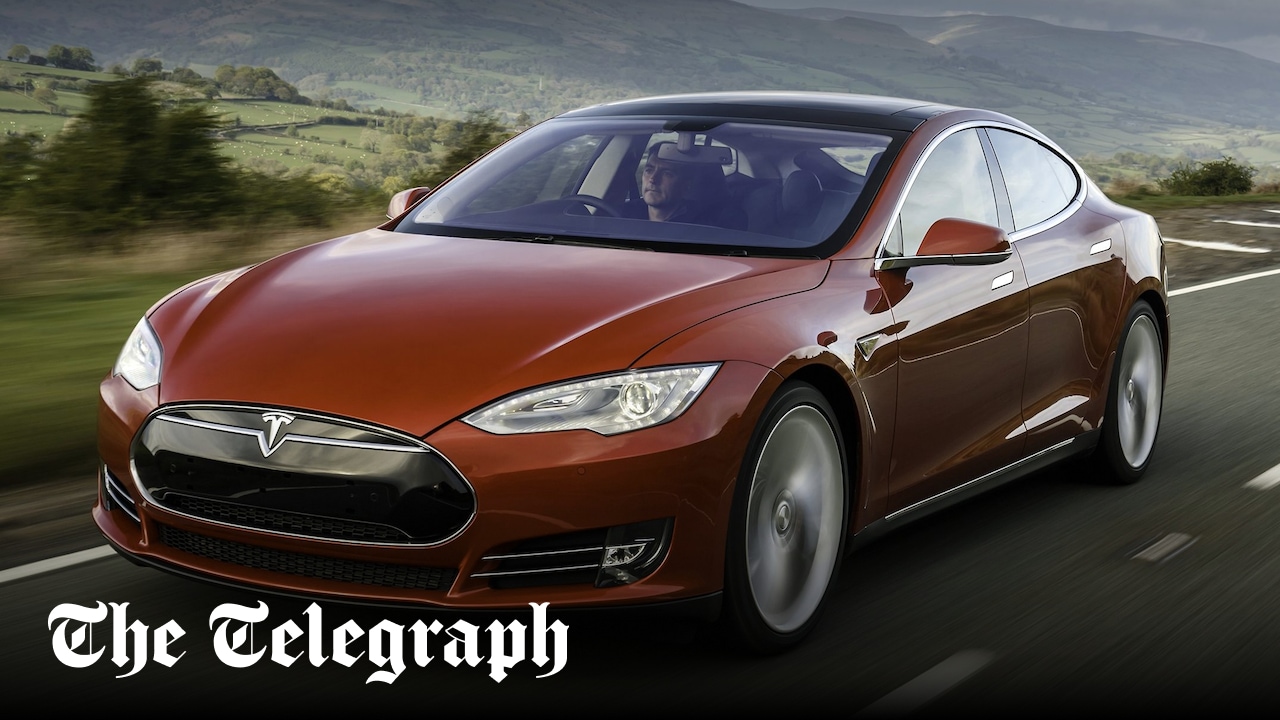
Tesla fixes software bug that allowed Chinese hackers to control car remotely
The Telegraph reported on Tesla's rapid patching of a software vulnerability that Chinese security researchers had demonstrated could enable remote vehicle control. Casey Ellis commented on the significance of the bug fix and Tesla's response to the security disclosure.
The CyberWire Daily Podcast 9.20.16
The CyberWire Daily Podcast episode from September 20, 2016, covers cybersecurity news including a Tesla vulnerability and patch. Casey Ellis is interviewed about the vulnerability disclosure and the importance of responsible reporting in automotive security research.
Tesla fixes software bug that exposed hacking vulnerabilities
Automotive News reported on Tesla's rapid software patch addressing a vulnerability that could have enabled remote access to vehicle systems. Casey Ellis contributed security research that helped identify the flaw and informed Tesla's remediation efforts.
Tesla Fixes Software Bug That Exposed Hacking Vulnerabilities
Bloomberg reported on Tesla's over-the-air software update that patched a vulnerability in its vehicles discovered by security researchers. Casey Ellis contributed to the identification and disclosure of the hacking vulnerability that Tesla addressed through the update.
Tesla fixes software bug that exposed hacking vulnerabilities
Tesla released a software patch to address a vulnerability that allowed remote vehicle control, as reported by the Chicago Tribune in September 2016. Casey Ellis contributed analysis on the security implications of the flaw and the importance of coordinated vulnerability disclosure in automotive systems.
Can bug bounty programs solve the cybersecurity workforce shortage?
Fedscoop published an interview with Casey Ellis on the "Hack the Pentagon" bug bounty program and its role in government cybersecurity. Ellis discusses how coordinated bug bounty initiatives can address workforce gaps and strengthen defensive capabilities across federal agencies.
Tesla fixes software bug that exposed hacking vulnerabilities
Industry Week reported in September 2016 that Tesla fixed a software bug exposing hacking vulnerabilities in its systems. Casey Ellis contributed to the reporting by highlighting how Tesla's collaboration with security researchers strengthened its vulnerability disclosure process and product security practices.
Hacking for investor profit
TechCrunch published an opinion piece by Casey Ellis on September 20, 2016, addressing ethical concerns in security research and disclosure practices. Ellis argues against researchers short-selling a company's stock before revealing vulnerabilities, referencing the St. Jude Medical and MedSec situation as a cautionary example.
Tesla fixes software bug that exposed hacking vulnerabilities
The Record reported in September 2016 that Tesla released a software update to fix a bug exposing its vehicles to potential hacking vulnerabilities. Casey Ellis contributed insight on the security implications and Tesla's response to the discovered flaw.