

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.

Why Cyber Pros With Compliance and Regulatory Knowledge Are In-Demand
Dice Insights published a career article examining why cybersecurity professionals with compliance and regulatory expertise command higher demand in the job market. The piece discusses how CISOs balance breach disclosure requirements and notes that compliance knowledge has become as essential as technical security skills for career advancement.

Threat Actors Don’t Punch in 9 to 5: Most Alerts Occur After Hours and on Weekends
This Security Boulevard press article, published September 25, 2025, examines Arctic Wolf's 2025 Security Operations Report, which finds over half of security alerts occur outside traditional business hours. Bugcrowd cofounder Casey Ellis says AI can handle repetitive, low-order tasks like alert triage, while human creativity and contextual understanding remain essential to SOC work.

Did Scattered Spider Scatter? Cyber Experts Are Skeptical
Security Magazine published an article questioning whether the Scattered Spider threat actor has truly disbanded after announcing retirement. Ellis is cited among cyber experts expressing skepticism about the group's claimed departure from ransomware operations.

CobaltStrike's AI-native successor, 'Villager,' makes hacking too easy
CSO Online published an article examining Villager, an AI-native successor to CobaltStrike that is freely available online. Casey Ellis discusses how the framework lowers barriers to conducting advanced cyberattacks by automating and accelerating malicious activities.

Security Industry Skeptical of Scattered Spider-ShinyHunters Retirement Claims
A SecurityWeek article examines industry skepticism about Scattered Spider and ShinyHunters' claims that they are retiring from cybercriminal activity. Casey Ellis comments on the credibility and reliability of such retirement announcements from threat actors in the cybercriminal underworld.

Fifteen Ransomware Gangs Retire, Future Unclear
Infosecurity Magazine reported in September 2025 that fifteen ransomware groups announced shutdowns on BreachForums. Casey Ellis commented on the significance of the retirements and assessed whether the closures represented genuine exits or strategic rebranding by the criminal organizations.

China-Linked AI Pentest Tool 'Villager' Raises Concern
Hackread published a report on Villager, a China-linked AI penetration testing tool that has accumulated over 10,000 downloads and raised cybersecurity concerns. Casey Ellis commented on the security implications of the tool's widespread adoption and its potential risks to enterprise environments.

Threat Group Scattered Lapsus$ Hunters Says It's Shutting Down
Security Boulevard reported on the Scattered Lapsus$ Hunters threat group's announcement that it is shutting down operations. Casey Ellis commented on law enforcement pressure as a driving factor and assessed the likelihood that the actors will reorganize under new identities rather than cease criminal activity entirely.

Sponsored: The challenge of managing browser extensions
Risky Business published a sponsored interview segment in which Casey Ellis discusses browser extension security challenges with David Cottingham and Daniel Schell from Airlock Digital. Ellis explores the risks and management strategies associated with browser extensions in enterprise environments.

AI Emerges as the Hope—and Risk—for Overloaded SOCs
SecurityWeek published an article examining AI's dual role in addressing and complicating security operations center workload challenges. Casey Ellis discusses how AI tools can help overwhelmed SOC teams manage alert fatigue while noting the risks of over-reliance on automated systems without proper human oversight.

BarCode Podcast Episode #125: Revelation
BarCode Podcast Episode #125, titled "Revelation" and hosted by Chris Glanden, explores vulnerabilities, truths, and the role of hackers in exposing hidden information. Casey Ellis discusses how hackers contribute to revealing security weaknesses and the broader implications of vulnerability disclosure.

Russian Threat Group Targets Microsoft Outlook With Malware
Security Magazine reported on research identifying a new Outlook backdoor deployed by a Russian-linked persistent threat group. Casey Ellis provided analysis of the threat's operational scope and implications for enterprise email security.

Sponsored: Why prompt injection is an intractable problem
Risky Bulletin published a sponsored interview in which Casey Ellis discusses prompt injection challenges with Keith Hoodlet, director of engineering at Trail of Bits. Ellis and Hoodlet examine why prompt injection remains a persistent technical problem in AI systems and explore potential mitigation approaches.

'NotDoor' malware tied to Russia's APT28 exploits Microsoft Outlook
SC Media reported on NotDoor malware linked to Russia's APT28 group that exploits Microsoft Outlook vulnerabilities. Casey Ellis provided analysis and context on the threat's implications for enterprise security and incident response strategies.

Beyond AI: What Trends Are Shaping a Cybersecurity Education
Dice Insights published an article examining how cybersecurity education is evolving as AI transforms the industry and entry-level positions disappear. Casey Ellis discusses the broader skill sets and hands-on experience aspiring professionals need to develop competitiveness in the changing landscape.

Sponsored: Push Security on the evolution of phishing techniques
A sponsored interview on Risky Business features Casey Ellis discussing phishing technique evolution with Push Security co-founder Jacques Louw. Ellis explores how Push Security's browser plugin addresses modern phishing threats and attack methods.
UK Government Drops Apple Encryption Backdoor Plans After Consultation With US Leaders - CPO Magazine
This CPO Magazine article reports that the UK government has dropped its plan for an Apple cloud encryption backdoor, per a statement from US Director of National Intelligence Tulsi Gabbard. Casey Ellis, founder of Bugcrowd, calls the reversal a big win for cybersecurity and says weakening everyone's security is a universally bad solution.

How Cybersecurity Pros Can Use AI Skills to Reduce Alert Fatigue
A Dice Insights article examines how cybersecurity professionals can apply AI skills to address alert fatigue from growing threat notifications. Casey Ellis contributes perspective on using AI to reduce noise and enable security teams to focus on higher-value work.

U.K. Backs Down on Apple Encryption Backdoor
A SecureWorld news article reports that the United Kingdom has withdrawn its demand for Apple encryption backdoors following U.S. pressure. Casey Ellis is quoted discussing the implications of the policy reversal for encryption standards and digital privacy protections.

Britain Drops Apple 'Backdoor' Demand After U.S. Pushback
A piece published by Information Security Buzz covers Britain's decision to withdraw its demand for Apple encryption backdoors following U.S. opposition. Casey Ellis is quoted commenting on the policy reversal and its implications for technology security standards.

UK rescinds order that required backdoor to Apple cloud data
A SC Media article from August 2025 reports on the UK's decision to rescind an order requiring a backdoor to Apple cloud data. Casey Ellis provides commentary on the implications of the regulatory reversal and encryption policy.

Would you hire a hacker?
ComputerWeekly.com published "Would you hire a hacker?" examining unconventional talent recruitment amid rising cyber breaches and security skill shortages. Casey Ellis discusses hiring reformed hackers and non-traditional backgrounds as a practical approach to addressing the cybersecurity talent gap.

Casey Ellis, Founder of BugCrowd: When Known Vulnerabilities are Life or Death
The Decibel Podcast featured Casey Ellis, founder of BugCrowd, in an episode examining the critical importance of addressing known vulnerabilities before they become systemic threats. Ellis discusses how unpatched and disclosed vulnerabilities pose significant risks to organizations and the broader security landscape.
Hackers Welcome: How One Government Agency Got It Right
At DEF CON 33, Casey John Ellis discussed how a government agency successfully welcomed good-faith hackers and built a constructive vulnerability disclosure program.
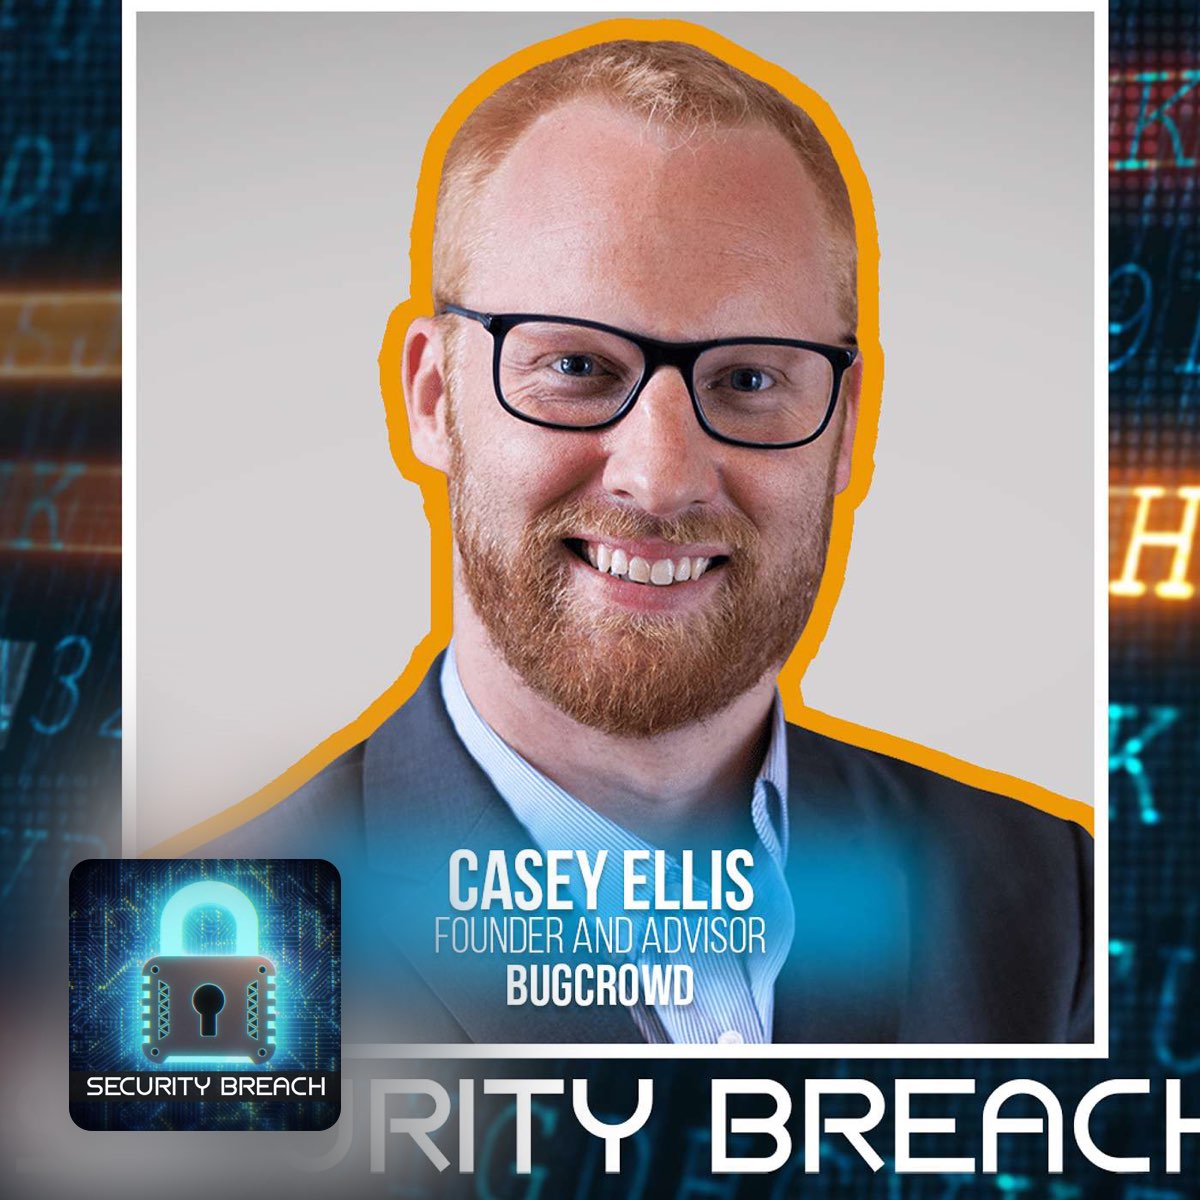
Being 'Proactively Paranoid, Not Paralyzed'
This Security Breach podcast episode, published August 8, 2025, features a discussion on industrial cybersecurity priorities with guest Casey Ellis, Founder and Chief Strategy Officer of Bugcrowd. Ellis discusses threats from initial access brokers and state-sponsored hackers, how Bugcrowd promotes white hat hacking, and how thinking like a criminal strengthens defenses through penetration testing.

CISA, Coast Guard Hunt Engagement Offer Path to Protect Critical Infrastructure
Security Boulevard reported on joint "hunt-forward" engagements launched by CISA and the U.S. Coast Guard to detect and disrupt cyber threats targeting critical U.S. infrastructure sectors. Casey Ellis contributed insights on how federal and private sector partnerships strengthen cyber resilience through proactive threat detection and intelligence sharing.
The Two Types of Fool — Generations in Cybersecurity
Casey John Ellis presented a BSides Las Vegas session about intergenerational knowledge sharing, intellectual humility, and practical wisdom in cybersecurity.
The Emerging Ecosystem Dedicated to AI Accountability - Decipher
This Decipher article, published August 5, 2025, examines an emerging ecosystem of security researchers who assess data security and privacy issues in AI systems. Casey Ellis, chief strategy officer at Bugcrowd, says the AI assessment ecosystem is still forming and growing rapidly, noting that generative AI is harder to define as vulnerable.

Corridor raises $5.4M, hires Alex Stamos as security leader
Axios reported on Corridor's $5.4 million funding round and Alex Stamos's appointment as security leader on August 5, 2025. Casey Ellis participated as an angel investor in the funding round for the AI security startup.

Vibe Coding: When Everyone's a Developer, Who Secures the Code
SecurityWeek published "Vibe Coding: When Everyone's a Developer, Who Secures the Code?" on August 5, 2025. Casey Ellis discusses the security challenges that emerge as development tools become more accessible to non-traditional developers and addresses the responsibility for code security in this shifting landscape.