

Casey Ellis, on the record.
1,355 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
Cisco Wireless LAN Controllers under threat again after critical exploit details go public
A CSO Online article published June 3, 2025, reports on a critical Cisco Wireless LAN Controller flaw, rated CVSS 10 out of 10, after exploit details became public. BugCrowd founder Casey Ellis calls the bug a textbook example of hardcoded secrets and weak validation, and says security teams should patch immediately.

Cisco IOS XE bug rated 10.0: 'Waiting is not an option'
A SC Media article from June 2025 discusses a critical Cisco IOS XE vulnerability rated 10.0 in severity. Casey Ellis is quoted providing perspective on the urgency and implications of the flaw for affected organizations.

Exploitation Risk Grows for Critical Cisco Bug
Dark Reading reported on the rising exploitation risk for a critical Cisco vulnerability. Casey Ellis commented on the threat landscape and the factors driving increased weaponization of the flaw in active attacks.

Sponsored: HD Moore on why vuln scanners are awful and broken
Risky Business published a sponsored interview in which Casey Ellis speaks with runZero founder and CEO HD Moore about the limitations and failures of vulnerability scanners. Ellis conducts the discussion as part of Risky Business Media's interview programming.

Indian Police Arrest Copycats of Myanmar Biz Model
Indian police arrested a cybercrime gang that replicated a Myanmar-based business model for financial fraud, as reported by Dark Reading. Casey Ellis provided commentary on the operation's tactics and how such cross-border schemes adapt criminal methodologies across regions.

NIST's LEV Equation to Rate Chances a Bug Was Exploited
NIST's LEV Equation to Rate Chances a Bug Was Exploited, published by Dark Reading, explains a new NIST framework for assessing the likelihood that a vulnerability has been actively exploited. Casey Ellis is quoted discussing the practical implications of the LEV equation and its application to vulnerability prioritization in real-world security operations.

Tracking Accusations May Have Roblox Back in Court
A Security Boulevard article examines allegations that Roblox secretly tracked children's data without consent, potentially violating federal privacy law. Casey Ellis discusses the privacy implications of the tracking practices and their broader significance for platform accountability.

Offensive Security Skills: What Cybersecurity Pros Need to Know
Dice Insights published an article on offensive security skills that cybersecurity professionals need to develop. Casey Ellis discussed how offensive security is becoming increasingly important as attacks and AI reshape the threat landscape and career opportunities for security professionals.

TeleMessage Signal app lands on CISA's exploited vulnerability list
TeleMessage's Signal app vulnerability was added to CISA's list of exploited flaws, according to reporting by SC Media. Casey Ellis commented on the significance of the vulnerability being tracked by federal authorities and its implications for enterprise security practices.

CISA Adds TeleMessage Vulnerability to KEV List
Hackread reported on CISA's addition of a TeleMessage vulnerability to its Known Exploited Vulnerabilities list. The article covers the security agency's ongoing efforts to track and document actively exploited flaws affecting critical infrastructure and government systems.

High Security Messaging App Tool Used by US Government Suspends Service After Security Breach - CPO Magazine
CPO Magazine's May 12, 2025 article reports that TeleMessage suspended TM SGNL, an unofficial Signal clone, after a security breach. Casey Ellis, founder of Bugcrowd, warns that secure messaging apps do not guarantee the security of their derivatives and add-ons, and hopes it becomes a prime example of why frameworks are no silver bullet.

Lawsuit alleges Roblox tracks children's data without parental consent
Security Magazine reported on a lawsuit alleging Roblox tracks children's data without parental consent. Casey Ellis characterized the case as highlighting the "trust tax" companies incur when mishandling user data, noting how consent complexity in digital environments may establish new legal precedents.

CISA adds the notorious Telemessage flaw to KEV list
CSO Online reported on CISA's addition of a Telemessage vulnerability to its Known Exploited Vulnerabilities list. Casey Ellis characterized the incident as a classic supply chain risk, noting that vendor security trust is essential and highlighting how a single vulnerability can have cascading impacts across dependent systems.

Bug Bounties, The Wanted Poster For Ethical Hackers - Future Secured Episode 35
Future Secured published a broadcast episode titled "Bug Bounties, The Wanted Poster For Ethical Hackers" on its Future Secured show. Casey Ellis discusses lessons from building Bugcrowd and explains how bug bounties function as a mechanism to coordinate ethical hackers toward organizational security objectives.

What the Netflix ‘Zero Day’ series got right about incident response
SC Magazine published Casey Ellis's perspective on Netflix's "Zero Day" series and its portrayal of incident response. Ellis notes that the series accurately captures the high-pressure environment of major incidents and the complex coordination required among technical teams, leadership, and government agencies.
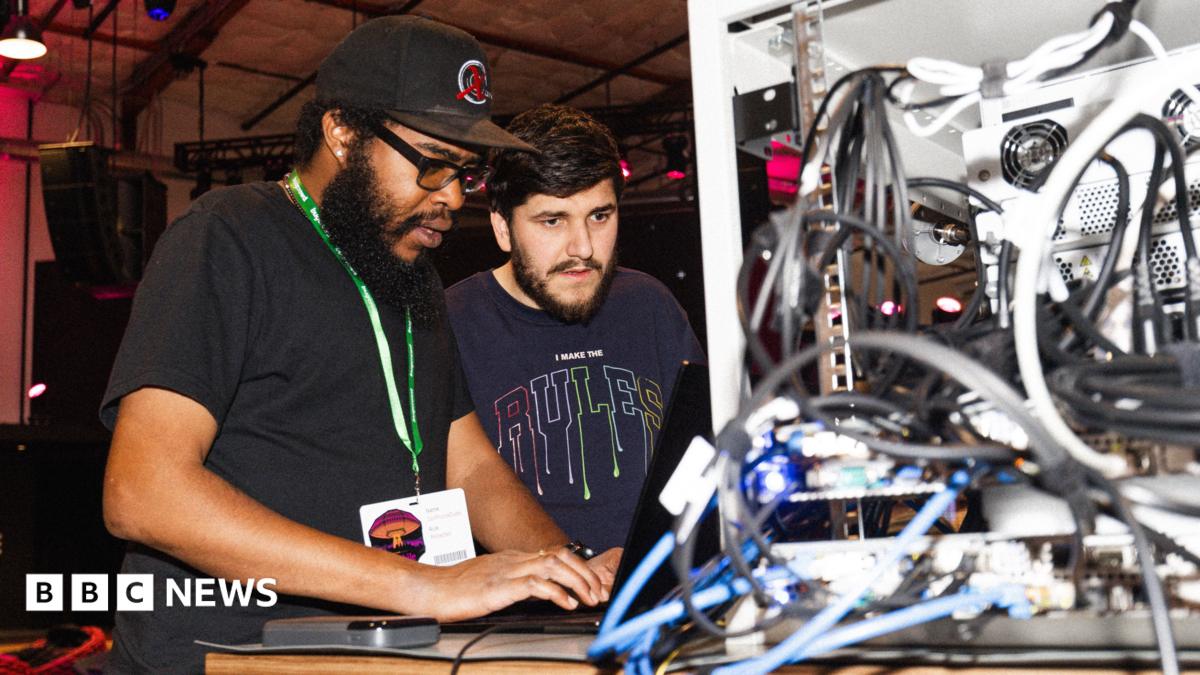
What is bug hunting and why is it changing?
This BBC News article from April 2025 explains how bug hunters are paid to find software flaws and how AI is changing their work. Bugcrowd founder Casey Ellis notes that bug hunters must operate within the law, and he observes that organizations racing to adopt AI often overlook what could go wrong.
Bipartisanship Key to CISA Renewal
This Security Boulevard article, from April 25, 2025, discusses the upcoming renewal of the Cybersecurity Information Sharing Act and urges Congress to pass it again. Bugcrowd founder Casey Ellis is quoted calling cybersecurity a team sport and saying the Act provides a safe framework that underpins public and private partnerships.

Why Vulnerability Exploitation Is Shifting in 2024-25
Dark Reading published an article examining how vulnerability exploitation tactics are changing in 2024-25. Casey Ellis argues that defenders have recently gained advantage through expanded bug bounty programs, improved disclosure practices, and more proactive vendor security efforts.
From Hacker to Founder, and Cybersecurity's Future
This April 21, 2025 podcast episode from Bare Knuckles and Brass Tacks features Casey Ellis in conversation with hosts George K and George A. He traces his move from hacker to solution architect to entrepreneur, including a marketplace linking ethical hackers with companies, and discusses why acquisition-focused security startups are hurting the industry.

CVE Program Gets Stay of Execution With Last-Minute Contract Extension for MITRE - CPO Magazine
CPO Magazine's April 17, 2025 article reports that MITRE received a federal contract extension just before its CVE program contract expired April 16. Casey Ellis, Bugcrowd founder, says continued US funding past early 2026 is not entirely out of the question, since disrupting the CVE program would pose a real national security threat.

Senators Urge Cyber-Threat Sharing Law Extension Before Deadline
This Infosecurity Magazine article, published April 17, 2025, reports that senators are urging Congress to extend the Cybersecurity Information Sharing Act for 10 years before its September sunset. Casey Ellis, founder of Bugcrowd, is quoted saying the act provides a safe framework that underpins public-private sharing and community sharing through US-based ISACs.

Bipartisan bill would renew cyber threat info sharing law
CIO Dive reported on a bipartisan bill to renew the Cybersecurity Information Sharing Act. Casey Ellis stated that the legislation is crucial for reinforcing the public-private trust framework essential for national cybersecurity.

Possible National Security Crisis Averted: CISA's Reversal Extends Support for CVE Database
This TechRepublic article, published April 16, 2025, reports that CISA executed the option period on MITRE's contract to keep the CVE vulnerability database running. Casey Ellis, founder of Bugcrowd, tells TechRepublic that CVE underpins vulnerability management and incident response, and that a sudden interruption could become a national security problem.
11th-Hour Funding Saves Program That Tracks Software Vulnerabilities
This PCMag UK article from April 16, 2025, reports that CISA extended MITRE Corporation's contract to administer the CVE Program, but only for 11 months. Casey Ellis, founder of Bugcrowd, says the close call has put a dent in confidence in the CVE process and points to a systemic issue in managing vulnerabilities.
MITRE warns of lapse with CVE program as contract with US set to expire
This April 16, 2025 article from The Record reports that MITRE warned its stewardship of the CVE program may end that week after the federal government declined to renew its contract. Casey Ellis, founder of Bugcrowd, is quoted saying a sudden interruption to CVE could quickly become a national security problem.
Slopsquatting: The Newest Threat to Your AI-Generated Code
The New Stack article, published April 16, 2025, examines slopsquatting, a risk where AI code generators suggest nonexistent package names that attackers can register. Casey Ellis, founder of Bugcrowd, tells the publication that developers are focused on making code work rather than preventing unintended behavior, a misalignment AI code generation accelerates.

In a Social Engineering Showdown: AI Takes Red Teams to the Mat
Security Boulevard published this April 16, 2025 article, In a Social Engineering Showdown: AI Takes Red Teams to the Mat, which examines AI-driven social engineering. Casey Ellis, Bugcrowd founder, says humans adapt better to human targets, but AI agents can operate at scale, so AI tends to perform better when breadth matters.

CISA at the Last Minute Extends Funding for Crucial MITRE CVE Program
This April 2025 Security Boulevard article covers uncertainty over government funding for MITRE's CVE vulnerability program and a new nonprofit introduced by CVE Board members. Casey Ellis, founder of Bugcrowd, says CVE underpins much of vulnerability management and critical infrastructure protection, and that a sudden service interruption could become a national security problem.
MITRE warns that funding for critical CVE program expires today
This BleepingComputer news article reports that MITRE warned U.S. government funding for the CVE and CWE programs was due to expire. Casey Ellis, founder of Bugcrowd, says CVE underpins vulnerability management, incident response, and critical infrastructure protection, and warns that a sudden interruption could become a national security problem.
MITRE set to lose funding today, CISA intervenes
Security Magazine's April 16, 2025 article reports that CISA has extended MITRE's funding, and security leaders share their views on the move. Casey Ellis, founder of Bugcrowd, warns that CVE underpins much of vulnerability management, incident response, and critical infrastructure protection, so a sudden interruption could quickly become a national security problem.